


RFID Systems


Academic RFID systems notes covering RF coupling, LF/HF/UHF, tag and reader architecture, standards, UID/byte order, host protocols, anti-collision, middleware, databases, access control, security, and verification.
RFID systems extend beyond tags and readers that exchange identifiers over radio. An end-to-end implementation spans the RF physical layer, air-interface protocol, reader-to-host communication, event processing, data modeling, authorization, security, and—where relevant—physical actuation.
These notes cover LF/HF/UHF operation, inductive coupling and backscatter, active and passive tags, ISO/IEC and GS1 standards, UID representation, serial communication, anti-collision, middleware, databases, access control, keyboard-wedge/HID readers, security, troubleshooting, SDR-based observation, and analysis of RFID event data from a systems-engineering perspective.
In an RFID application, “the tag was read” is not a complete system state. The reader and antenna that produced the observation, repetition count, event time, canonical identifier representation, authorization result, and confirmation of the physical action may all need to remain distinct. In access-control systems in particular, UID, authentication, and authorization must not be treated as synonyms.
Historical details about specific reader models, wiring problems, and early device-integration work are kept on the Afyon Kocatepe University IT internship page. The course focuses on the technical principles, standards, and system-design lessons that can be generalized beyond those devices.
Unit 1: RFID from a systems-engineering Perspective
1.1. Definition and Scope of RFID
Radio-Frequency Identification is a family of technologies for automatically identifying a card, tag, or physical object through radio-frequency communication. In a basic interaction, a reader creates an RF field or transmits a query, and a tag responds according to its technology and protocol with an identifier or stored data.
The difference from a barcode is not simply that RFID is wireless. Depending on the system, RFID can:
- work without direct line of sight,
- identify multiple tags in the same field,
- support writable tag memory,
- automate identification events,
- maintain a machine-readable relationship between a physical asset and a digital record.
The trade-off is a new set of problems: RF propagation, collision, unintended reads, privacy, cloning, reader placement, and protocol interoperability.
1.2. Distinction Between RFID and Identity Systems
RFID is often an input to an identity system, not the entire identity and authorization system.
These statements are not equivalent:
card UID = 04A1B2C3and
this card belongs to this user and is currently authorized to open this doorThe second statement requires card state, assignment, subject identity, permissions, time constraints, and—where required—additional authentication.
1.3. The automatic-identification Chain
A useful end-to-end model is:
physical tag
→ RF link
→ reader
→ device protocol
→ host interface
→ parsing / normalization
→ application logic
→ database
→ decision
→ log / alert / physical action
Application software is responsible for the middle of this RFID chain: obtaining reader data reliably, converting the identifier into a canonical representation, relating it to persistent identity/authorization state, and turning the result into an application or physical-control decision.
Unit 2: Core Components of an RFID System
RFID component selection involves more than whether a tag can be read. Define range, surrounding materials, tag orientation, and expected simultaneous tag count. Verify frequency and protocol compatibility across reader, antenna, and tag, then measure read probability in the actual installation. Success with one tag in a laboratory does not guarantee equivalent performance near metal or with multiple tags.
2.1. Tag
An RFID tag contains at least an antenna/coupling element and electronic circuitry that carries identity or application data. Its resources vary significantly by RFID family and power model.
A tag can expose information such as:
- chip/manufacturer identity,
- UID/TID-like identifier,
- application memory,
- an EPC or other object identifier,
- access/protection fields,
- sensor data.
These fields and their security properties are not universal across all RFID technologies.
2.2. Reader
A reader is not just a device that “returns a card number.” On the RF side it communicates with tags; on the application side it transfers data to a computer or controller.
Depending on the protocol and product, a reader may:
- create the RF field,
- interrogate tags,
- perform anti-collision/arbitration,
- read or write memory regions,
- perform error checking,
- report timing/antenna metadata,
- connect over serial, USB, Ethernet, or another host interface.
The boundary most visible to application developers is often the reader-to-computer interface. The RF transaction may terminate inside a commercial reader; host software must still understand framing, device state, timeout, and error semantics correctly.
2.3. Antenna
The antenna controls how RF energy is radiated and received. Gain, directivity, polarization, mounting, and surrounding materials can change the read zone substantially.
A compatible reader does not guarantee a successful deployment. The same reader can behave very differently when the antenna geometry, orientation, cable loss, or surrounding metal changes.
2.4. Back End and Middleware
Enterprise RFID systems commonly place processing between readers and business tables:
- device adapters,
- event collection,
- duplicate filtering,
- validation,
- authorization,
- logging,
- database access.
This layer matters because a tag can be observed repeatedly while it remains in the RF field. Treating every RF observation as a separate business event can corrupt access or inventory data.
Unit 3: Active, Passive, and semi-passive Tags
3.1. Passive Tags
A passive tag has no continuously available internal power source. It harvests operating energy from the reader field and communicates within that limited energy budget.
Consequences include:
- potentially low cost and small form factor,
- no battery-maintenance cycle,
- constrained computation and memory,
- read range and reliability that are sensitive to the RF environment.
3.2. Active Tags
An active tag has its own energy source. That can support greater range, periodic transmission, additional processing, or sensors. Battery lifetime, maintenance, size, and cost then become system requirements.
3.3. Semi-passive Tags
Semi-passive designs can use a battery for internal circuitry while still relying on energy from the reader for parts of the communication process. Vendor terminology varies, so the engineering question should be the actual power and communication model, not only the marketing category.
3.4. Tag Selection Is a System Decision
Selection should follow requirements such as:
- read distance,
- data capacity,
- object speed,
- proximity to metal or liquid,
- temperature/humidity,
- battery lifetime,
- unit cost,
- security,
- write frequency.
The tag with the longest range is not automatically the best tag.
Unit 4: Frequency Bands and Electromagnetic Coupling
Operating-frequency selection considers propagation, antenna size, local regulatory limits, and installation conditions. Once an appropriate band is chosen, evaluate antenna placement and blind zones before simply increasing power. With several readers in one area, check interference and scheduling. Performance includes avoiding unwanted reads outside the intended zone, not only successful reads at maximum distance.
4.1. LF, HF, and UHF
RFID systems operate in several frequency families. Common examples include:
- LF around 125/134 kHz,
- HF at 13.56 MHz,
- UHF in the regional 860-960 MHz family,
- microwave bands for some specialized systems.
The allowed channels and power limits depend on region and current regulation. Frequency affects antenna size, coupling, propagation, data rate, environmental sensitivity, and achievable range.
4.2. Inductive Coupling
In LF/HF near-field systems, magnetic coupling between reader and tag coils can dominate. A passive tag can harvest energy from this field and return data through techniques such as load modulation.
Practical behavior depends on:
- coil geometry,
- resonance,
- quality factor,
- tag orientation,
- nearby metal.
4.3. Backscatter
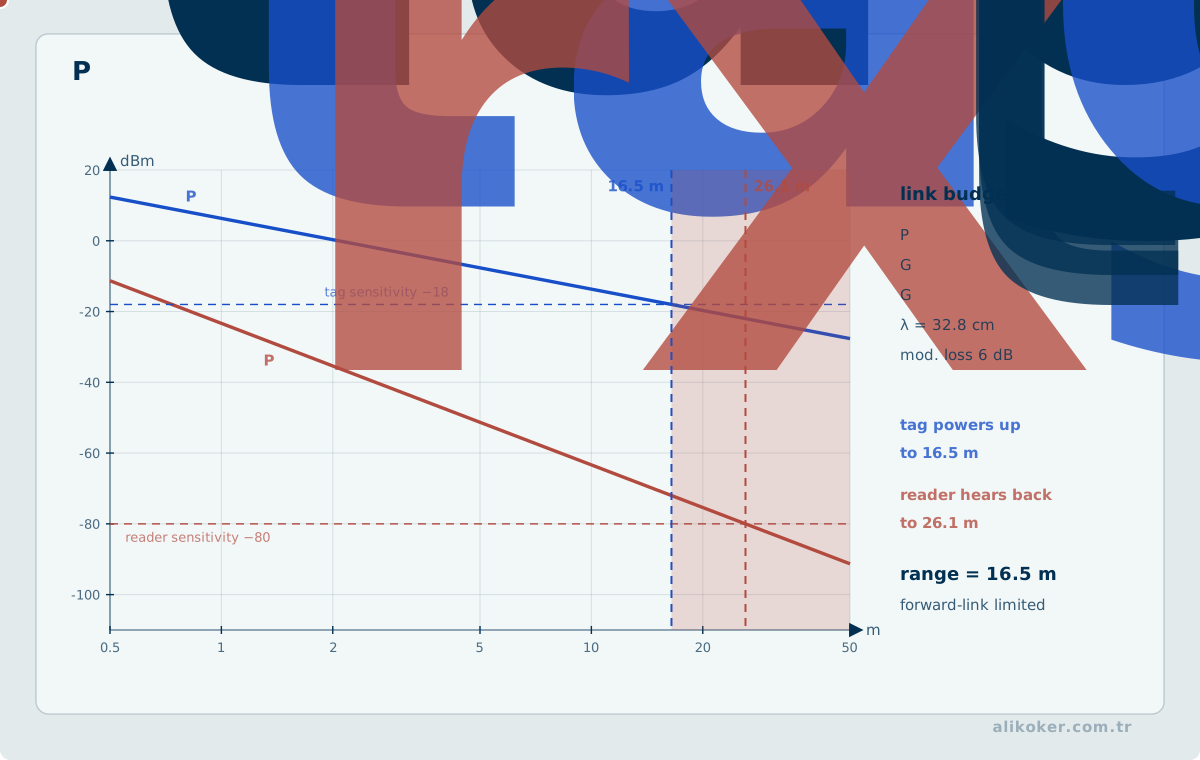
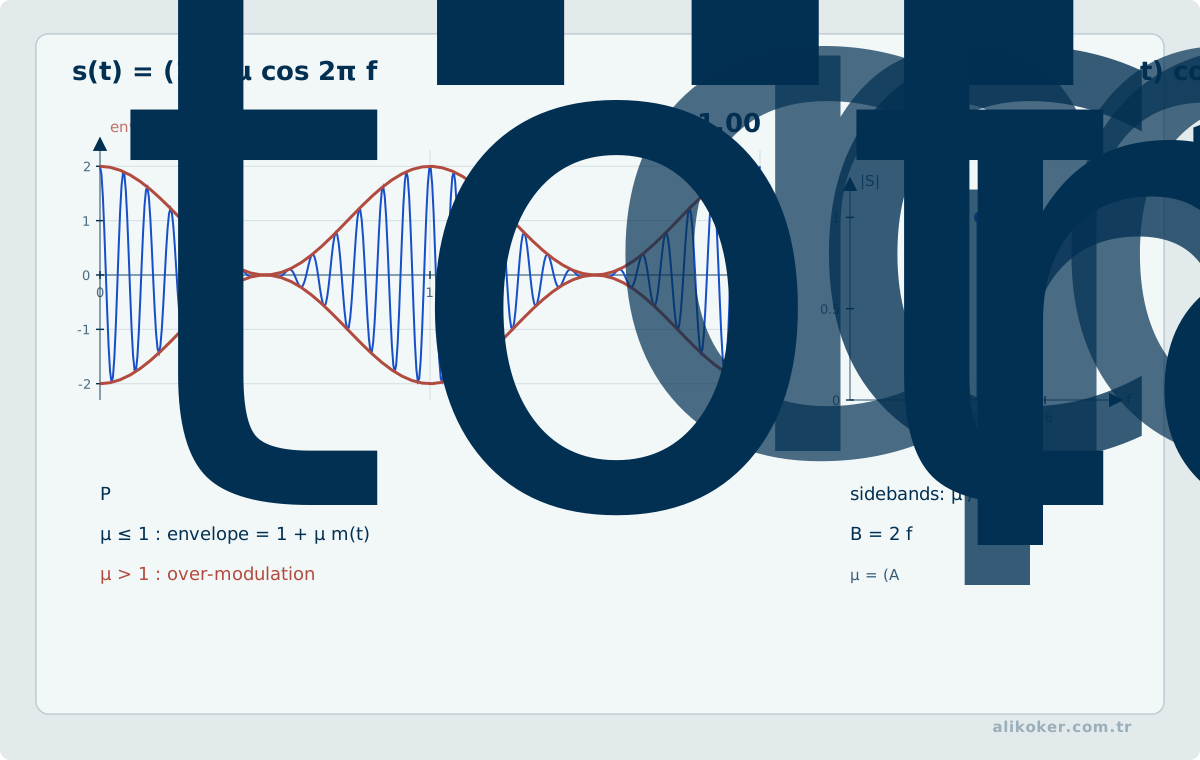
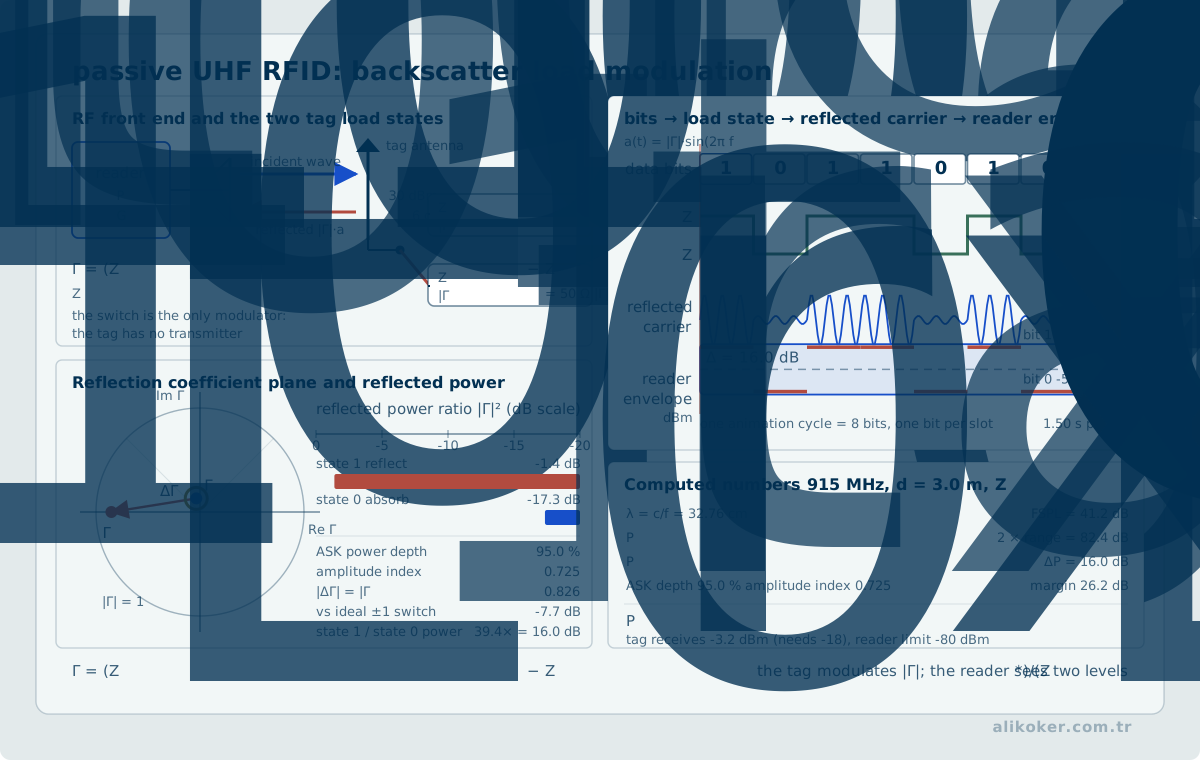
In UHF passive RFID, a tag can harvest energy from the reader's RF field and encode information by changing the reflection characteristics of its antenna. The reader observes the resulting backscattered signal.
This can enable longer read distances but makes link budget, orientation, multipath propagation, shadowing, and regional RF constraints more important.
4.4. Read Range Is Not a Constant
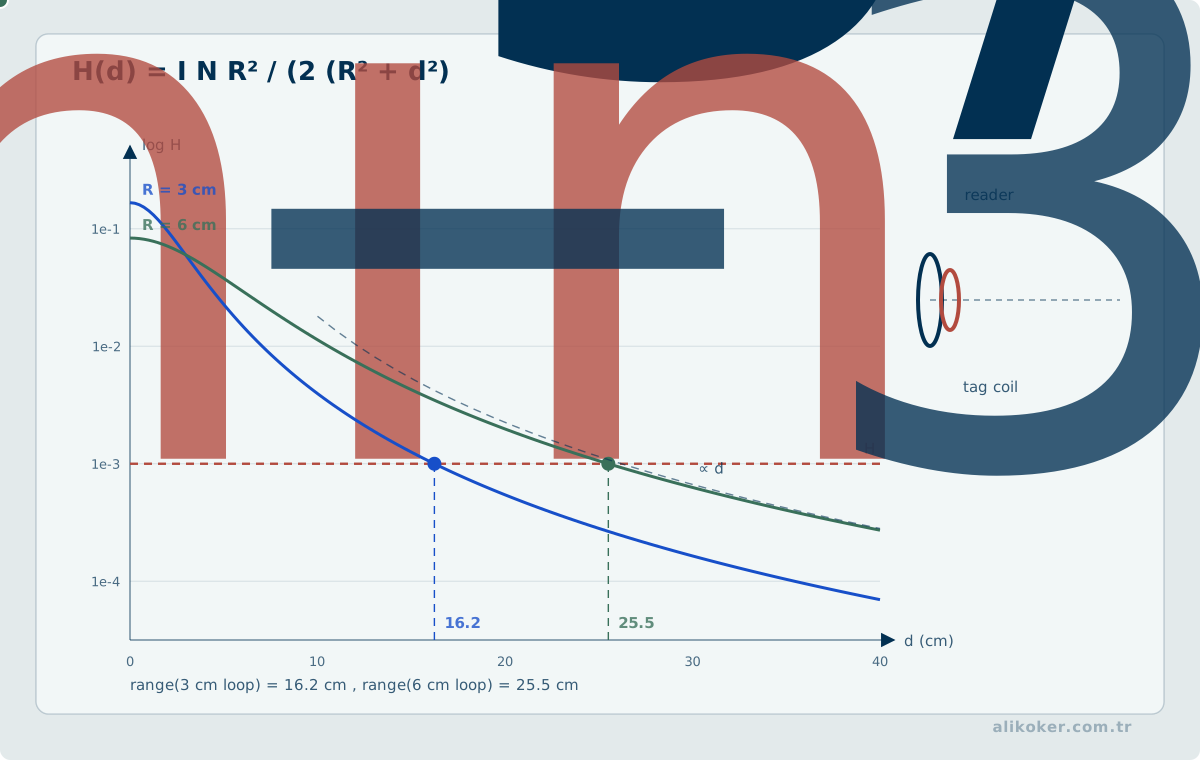
A catalogue value is not a field guarantee. Real range depends on:
- reader transmit power,
- antenna gain,
- cable loss,
- tag antenna efficiency,
- orientation,
- nearby metal/liquid,
- interference/noise,
- regulatory power limits.
Field validation is therefore part of engineering, not a final acceptance detail.
Unit 5: Standards and Interoperability
5.1. ISO/IEC 14443 and Proximity Cards
The ISO/IEC 14443 family is a major reference for 13.56 MHz proximity cards and contactless smart-card systems. Different parts of the family address physical properties, RF interface, and protocol behavior.
An application developer must still distinguish the air interface from the reader's host interface. A reader can terminate ISO/IEC 14443 internally and expose only a UID or processed fields over serial/USB.
5.2. ISO/IEC 15693
The ISO/IEC 15693 family covers contactless vicinity objects/cards. “Proximity” and “vicinity” represent different interface/use models, not merely alternative marketing terms.
5.3. ISO/IEC 18000 and UHF RFID
The ISO/IEC 18000 family defines RFID air interfaces for item management. UHF Type C systems are covered by ISO/IEC 18000-63.
Standard revisions should not be conflated across time. ISO/IEC 18000-63:2021 is a published edition, and any conformity claim should identify the exact revision used as the design baseline. A later edition cannot be projected backward onto an earlier implementation.
5.4. GS1 EPC Gen2
GS1 EPC Gen2 is a major UHF air-interface protocol family for supply-chain and object-identification applications. An engineering statement such as “Gen2 compatible” is incomplete without the revision, mandatory/optional features, memory-bank assumptions, supported commands, and interoperability profile used by the system.
5.5. What Standard Compatibility Does Not Guarantee
Supporting the same RFID standard does not guarantee:
- identical UID formatting,
- the same host protocol,
- the same security policy,
- the same driver/API behavior.
Different readers can support the same tag family while exposing different host protocols, framing rules, timeout behavior, and event models. RF-standard interoperability and application-programming interoperability are therefore separate concerns.
Unit 6: UID, Byte Order, and Representation
6.1. A UID Is a Byte Sequence
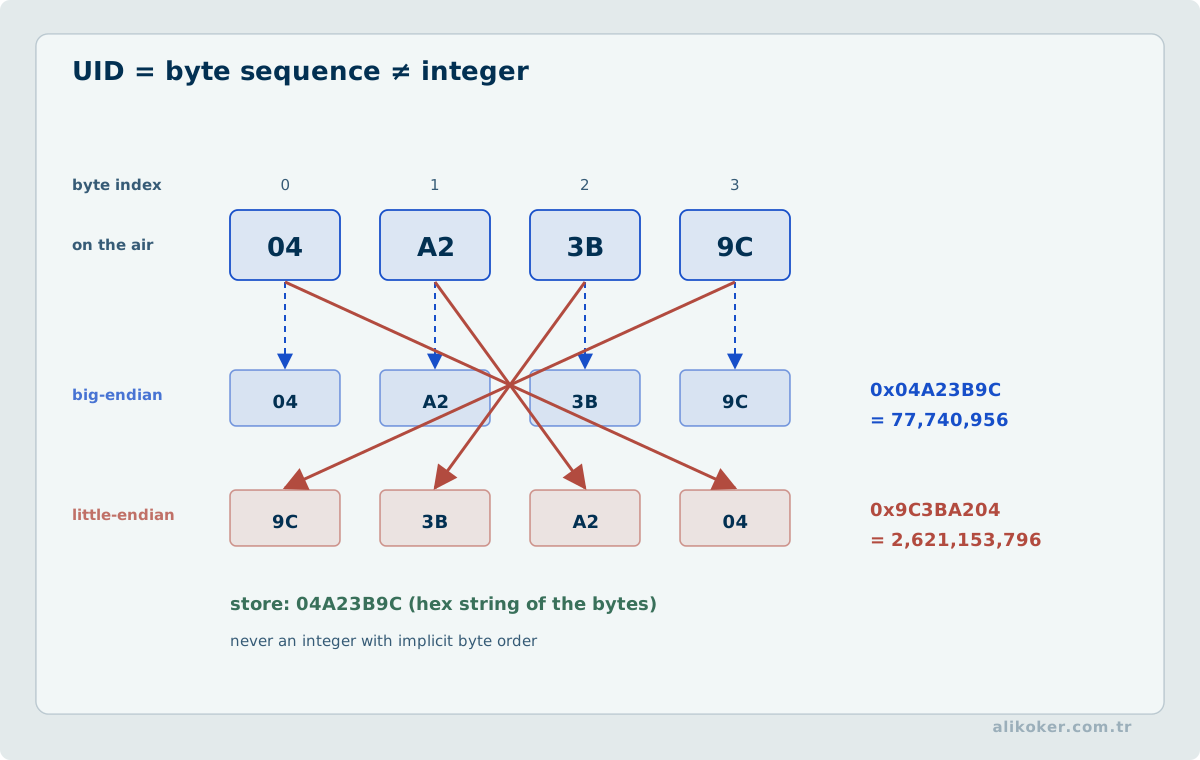
RFID identifiers are often rendered as hexadecimal text in user interfaces. At protocol level, however, the value is a sequence of bytes.
For example:
F2 3A CB D2may be displayed as:
F23ACBD2As a representation example, consider a reader that emits F23ACBD2 while a database stores the same four bytes as D2CB3AF2. The problem is not necessarily “the wrong card”; it can be a byte-order and representation contract mismatch.
6.2. Protocol Order Is Not Automatically CPU Endianness
These are separate concepts:
- byte order on the wire,
- device display convention,
- integer conversion in software,
- canonical database representation.
The system should document exactly where a conversion occurs.
6.3. UID Length Must Not Be Generalized
Some readers expose a four-byte identifier as eight hexadecimal characters. That is a device/application contract, not a universal RFID rule. Identifier length should be derived from the protocol family, tag type, and reader API rather than assumed globally.
That distinction remains explicit in the later keyboard-wedge/HID RFID reader study.
6.4. Canonical Representation
A clean application boundary can normalize input as:
raw bytes -> validation -> canonical uppercase hex -> database comparisonPresentation can add separators, but persistence and equality should not depend on UI formatting.
6.5. UID Byte Order and Identity Representation Contracts
An RFID UID can exist as the raw bytes read from a card, characters emitted by the reader driver, and a textual identifier stored by the application. Converting a four-byte example such as 04 A1 B2 C3 into an integer depends on big- or little-endian interpretation, zero padding, and unsigned-number semantics. UID length varies by technology; coercing every identifier into four bytes increases collision risk.
The data model preserves raw bytes with an explicit length alongside a derived human-readable representation. A keyboard-wedge device generating keystrokes does not provide cryptographic card authentication; destination focus and terminator characters require verification. UID alone should not be treated as strong proof of identity.
Unit 7: RS232 and reader-host Communication
7.1. Separate the RF and Host Boundaries
An RFID reader has two different communication boundaries:
card <-> reader : RF protocol
reader <-> computer : host protocol
The host side may be RS232, RS485, USB, Ethernet, keyboard-wedge/HID, or a vendor SDK.
For application software, the second boundary — between reader and host — is often the more visible one. It can involve UART/RS232, USB, HID, Ethernet, or a vendor API independently of the RF air interface.
7.2. Serial Parameters
A serial connection requires agreement on:
- baud rate,
- data bits,
- parity,
- stop bits,
- flow control.
A mismatch can result in no input or apparently random bytes.
7.3. MAX232 and Electrical Levels
Microcontroller UART logic levels are not the same as classical RS232 electrical levels. A level translator such as MAX232 can provide the physical conversion.
This is an important software-debugging distinction: successfully opening a COM port says nothing about whether the electrical interface is correct.
7.4. Framing
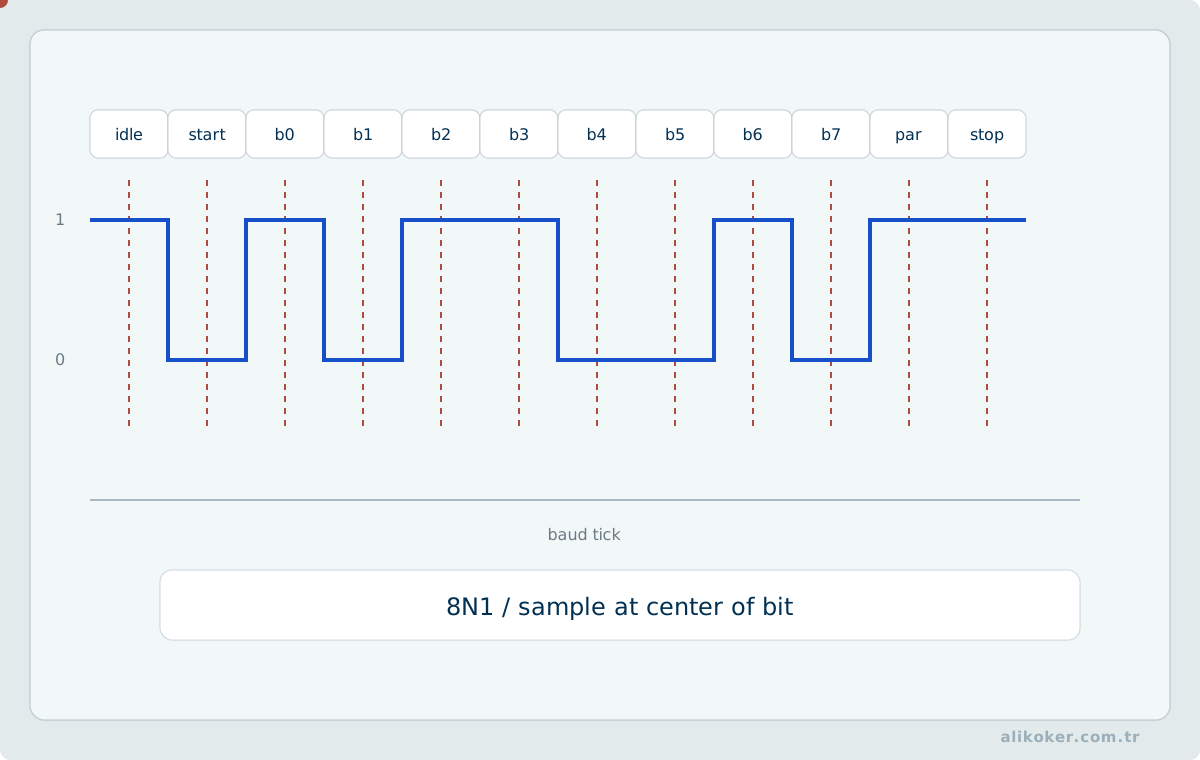
Some readers use control bytes such as STX/ETX:
STX | payload | ETXA serial DataReceived callback must not be treated as a packet boundary. A frame can be split across callbacks or multiple frames can arrive together.
A robust implementation uses an accumulator/parser or state machine.
7.5. Inspect the Raw Stream First
Before building higher layers, raw serial traffic should be verified with a terminal or protocol analyzer. This separates framing problems from parser or database defects. The first diagnostic question is:
What does the device actually send?
My Serial-Port Monitoring and Control Software grew out of this need.
Unit 8: Reader Integration and Device-Specific Protocols
An RFID standard may define the air interface between reader and tag without imposing one host protocol between the reader and application software. Device integration therefore begins by extracting the reader's host contract.
8.1. Stream-oriented Readers
Some readers emit data spontaneously when a tag is detected. The host must determine frame boundaries, fixed or variable length, checksum rules, text/binary encoding, and how consecutive reads are separated.
A stream parser must not assume that one read() call equals one RFID event. A frame may be split across multiple reads, or one buffer may contain multiple frames.
8.2. Request-response Readers
Other devices require the host to issue a command before returning status or an identifier. Transaction identity, timeout, retry, and the effect of repeated commands then become part of correctness. “No response received” and “command was not applied” are not equivalent states.
8.3. SDK- or command-tool-mediated Readers
Some commercial readers expose a vendor SDK, virtual COM layer, or command-line tool instead of a raw protocol. The application should not confuse stdout text or callback state with physical device state. Versioning, error codes, and reconnect behavior still need explicit modeling.
8.4. Adapter Architecture
A small adapter boundary can isolate device-specific code from application logic:
ReaderAdapter
  -> connect
  -> read/event
  -> health
  -> disconnect
Above the adapter, the event model should preserve identifier, source reader, read time, quality/confidence when available, and enough traceability to recover the raw input.
Specific reader models, wiring details, and historical implementations should not be generalized into course-wide behavior. The course retains only protocol, state, and fault-management principles that generalize beyond a device; the historical device record remains on the application page linked in the introduction.
Unit 9: Multiple Tags, anti-collision, and Event Modeling
9.1. More Than One Tag in the Field
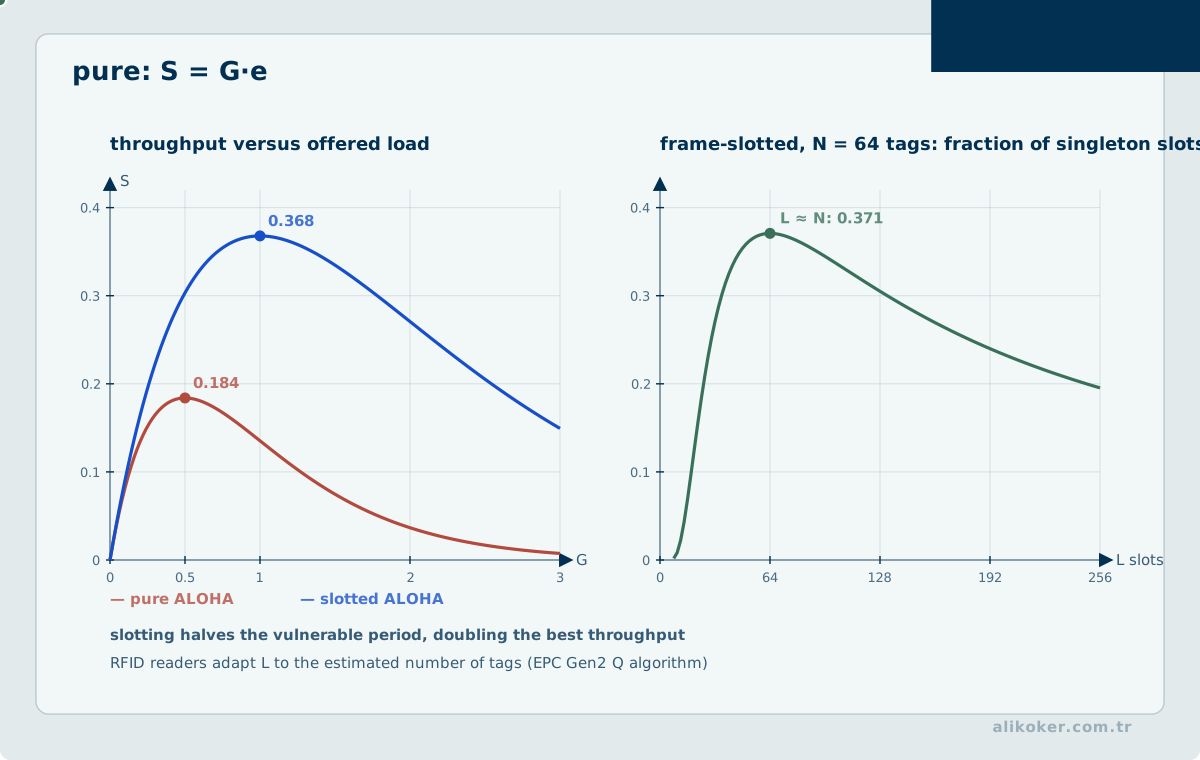
When several tags respond in the same reader field, the RF protocol needs a collision-arbitration mechanism. Modern RFID families use anti-collision procedures to identify tags individually.
Application-level duplicate events are a different problem.
9.2. Causes of Repeated UID Reads
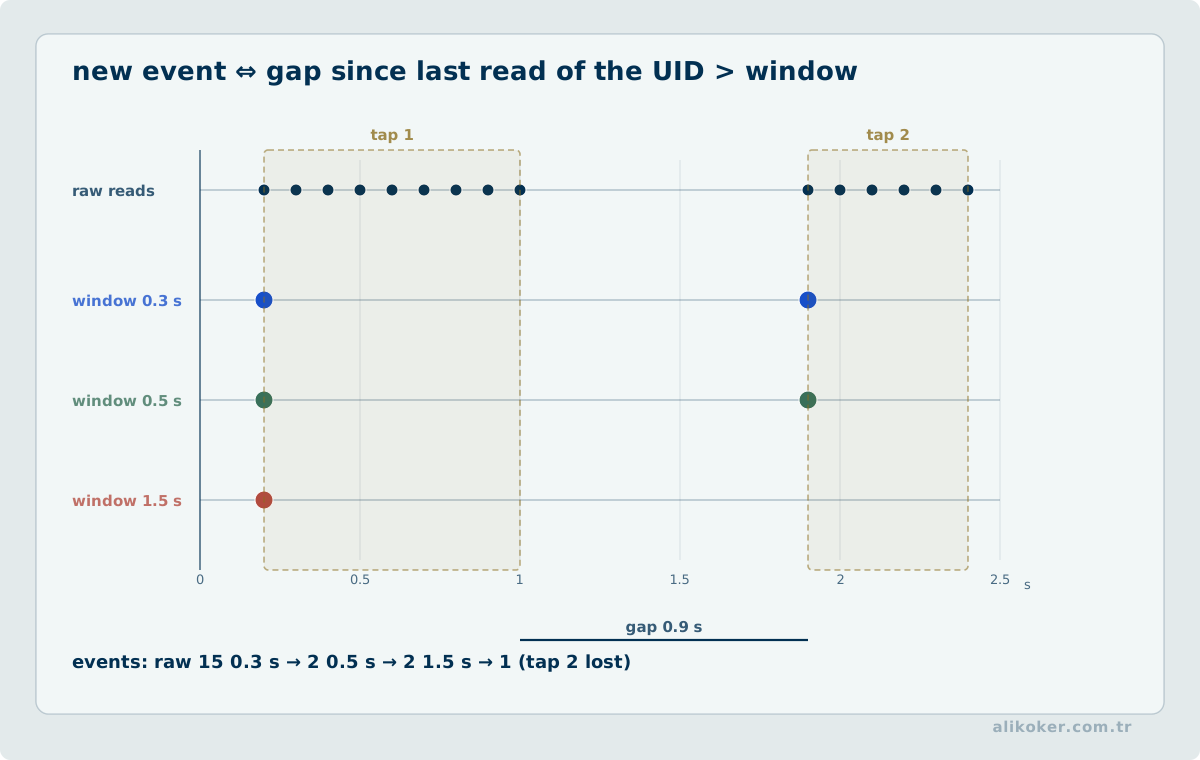
A card held in the read zone can generate repeated observations:
04A1B2C3
04A1B2C3
04A1B2C3
...
Treating all of them as separate access events can be wrong.
Depending on the application, the software may need:
- debounce,
- minimum repeat interval,
- card-present/card-removed state,
- reader-zone-based deduplication.
9.3. Event Context
A useful observation record can include:
readerId
antennaId
uid
timestamp
rawFrame
quality/rssi (when available)
device/protocol status
This preserves the difference between identity and observation context.
9.4. Ordering
In networked deployments, device timestamp and server-receive timestamp can differ. If ordering is operationally significant, the source and trust model of time must be explicit.
9.5. Collision, Queueing, and Read Capacity in RFID Environments
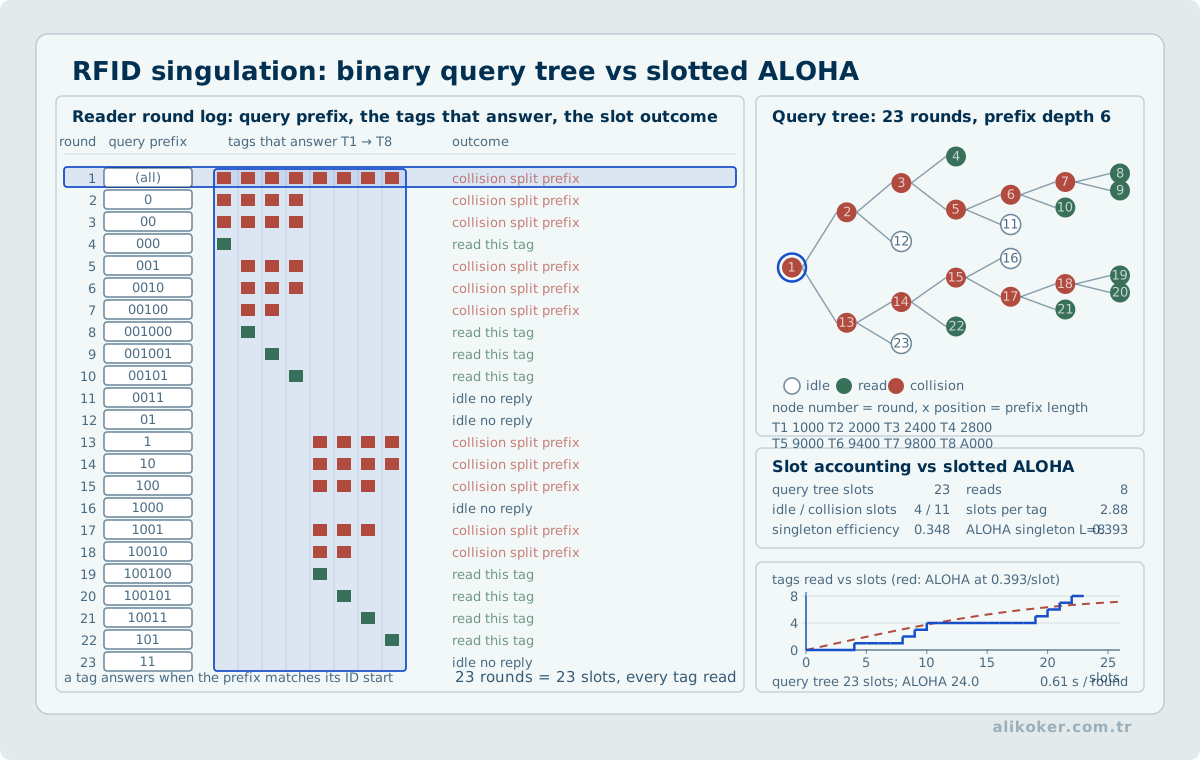
An RFID reader's air-interface capacity can be limited by collisions among tags responding in the same interval. Anti-collision round count and slot selection interact with tag density, radio conditions, and the speed of moving objects. Read capacity is better characterized by the fraction of distinct tags correctly identified within a bounded passage interval than by the raw number of inventory requests per second.
- Measure the nonlinear growth of anti-collision time as tag density increases.
- Evaluate per-reader service capacity together with tag arrival and visibility windows.
- Study how additional retries affect latency and channel utilization while improving read success.
9.6. Separating Identity from Events in Multi-Tag Reads
An RFID reader may report the same tag repeatedly while it remains in the antenna field. These observations do not automatically establish distinct physical passages. A raw read may contain (reader, antenna, uid, timestamp, signal); an application-level entrance event additionally requires a time window, direction, and passage rule. Suppressing repeated UIDs within a short window reduces duplicates but can also merge two genuine successive passages.
Air-interface anti-collision distinguishes multiple tags in the reader field; it does not replace event deduplication in application software. Reader-buffer overflow and intermittent antenna coverage can cause missing observations. Failure to read a tag does not prove that the tag was absent. Detection quality must be tested across antenna placement, reflection and metal effects, read rates, and motion speed.
A UID alone should not be treated as a strong authentication credential. Separately retaining raw observations and derived passage decisions makes false positives and missed detections auditable. Decisions should reference the reader identity, rule version, and observations from which they were inferred.
Unit 10: Middleware, Database, and Authorization
10.1. UID Is Not the User
A maintainable data model separates tag identity from the person or asset:
Tag(uid, status, type, ...)
    ↓
TagAssignment(tagId, subjectId, validFrom, validTo, ...)
    ↓
Person / Asset
    ↓
Permission
A lost card can then be revoked without deleting the person.
10.2. Metadata, Identity, and Authorization Data Model
An RFID event should contain more than a card_id. Source reader, event time, raw/canonical identifier, read result, and—where relevant—the authorization-policy revision should remain separable.
Identity and authorization are not the same concept. “Who does this identifier represent?” and “may that identity pass this resource at this time?” are different queries. Keeping them separate allows roles, time windows, zones, revocation, and other policy dimensions to evolve without redefining identity.
The database boundary should also enforce identifier normalization at one defined point. Device-specific byte order or text representation should not require different conversion logic in every query.
10.3. Authorization Decision
Even a simple access decision is more than a UID lookup:
is the card known?
→ is the card active?
→ is the subject active?
→ is access allowed for this door?
→ is the time policy satisfied?
→ is the system in a valid state?
→ allow / deny
The result and reason should be auditable.
10.4. Data Integrity
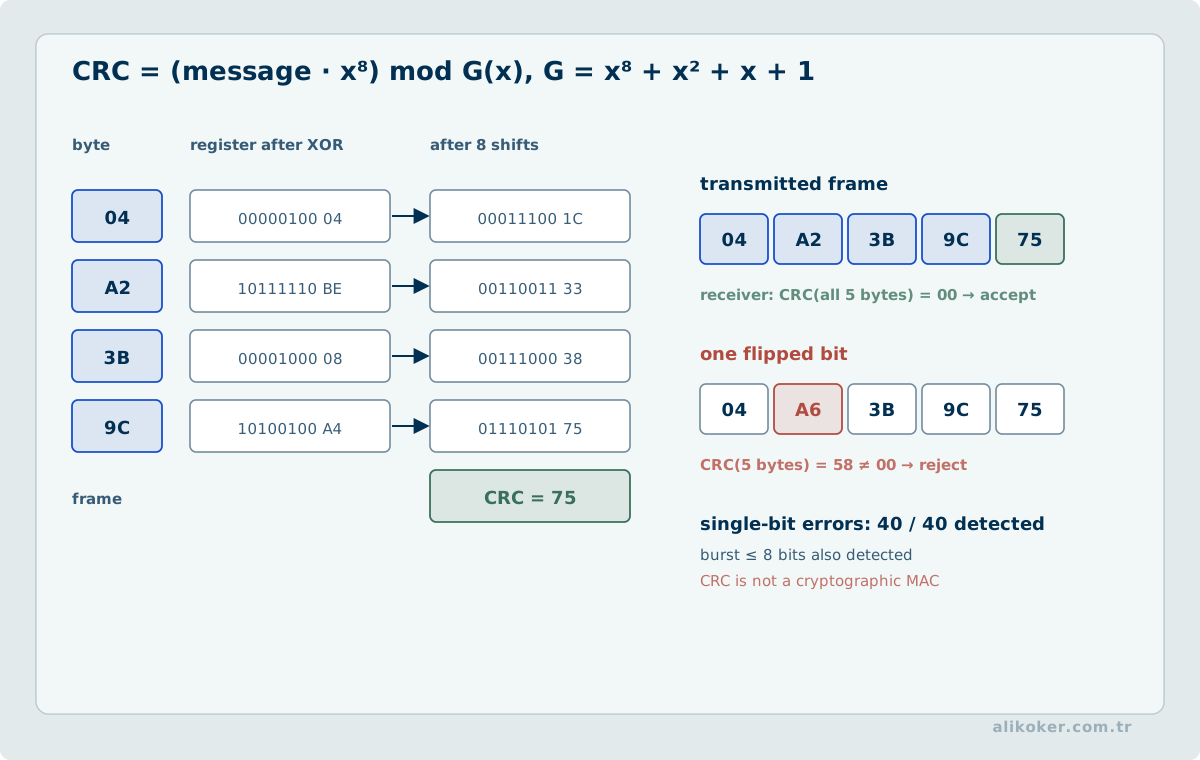
A duplicate UID record, wrong card assignment, or mutable access history can become a security issue. Database constraints and audit design therefore matter:
- uniqueness,
- referential integrity,
- controlled updates,
- audit trail,
- timestamps.
Unit 11: End-to-End Decision Chain in RFID Access Control
An RFID access-control system cannot be reduced to “open the door if a card is read.” A reliable decision chain separates physical acquisition, identity, authorization, actuation, and physical feedback.
11.1. Detection and Event Production
When the reader produces an identifier, the event is captured with source reader, timestamp, and sufficient raw-input context. Repeated reads are handled through an explicit debounce/deduplication policy.
11.2. Identifier Normalization
Byte order, hexadecimal representation, case, padding, or HID keyboard conversion is normalized before database lookup. Normalization rules should be configured and testable rather than hidden in scattered application code.
11.3. Identity and Authorization
The canonical identifier is first associated with an identity; authorization for the requested resource is evaluated separately. A decision can depend on identity, zone, time window, credential status, and policy revision.
11.4. Physical Command
The authorization outcome and the relay/turnstile/door command are distinct records. Producing an OPEN message does not prove that the physical transition occurred.
11.5. Physical Feedback
When actuator or door feedback exists, “command accepted,” “lock released,” “door opened,” and “door closed again” should be observable as separate events. The distinction matters for both security and fault diagnosis.
11.6. Audit Record
Audit records should include denied credentials, unknown identifiers, timeouts, reader disconnections, and manual interventions in addition to successful access. The system should be able to reconstruct why access was or was not granted.
The principle scales from a small prototype to an enterprise access-control system: decision, command, and physical outcome are different states.
Unit 12: Keyboard-wedge/HID RFID Readers
12.1. Not Every Reader Exposes a Serial Protocol
Some readers present the result to Windows as if they were keyboards. After handling the RF transaction internally, the device can “type” an eight-character hexadecimal identifier.
The software boundary then becomes:
RFID card
→ RF handling inside reader
→ keyboard-wedge / HID-like input
→ Windows input path
→ character sequence
→ UID parser
The application is no longer decoding the RF protocol.
12.2. Focus
A normal KeyDown handler can be enough for a focused kiosk form. More complex applications may evaluate:
IMessageFilter,WndProc,- Raw Input,
- low-level hooks only when truly required.
The correct boundary depends on focus guarantees and whether the software must prove which physical keyboard-class device produced the input.
12.3. Turkish Q/F Keyboard Layouts
One of the readers I used emitted a four-byte UID as eight hexadecimal keystrokes. The A-F key mapping behaved differently across Turkish Q and F layouts, so the application needed explicit mapping logic.
This detail illustrates a broader point: device “data” can be transformed by operating-system input layers before it reaches application code.
A current, deeper treatment is available in Reading a 4-Byte RFID UID Through a Keyboard-Wedge/HID Reader in .NET.
Unit 13: RFID Security and Privacy
13.1. A UID Is Not a Secret Key
The most important rule is:
a readable UID alone is not strong proof of identity.
A simple prototype can whitelist UIDs, but higher-risk systems must consider cloning, emulation, unauthorized reading, and stronger authentication.
13.2. Attack Surface
RFID security spans more than the air interface:
tag
↕
RF channel
↕
reader
↕
host protocol
↕
middleware
↕
application
↕
database
Possible threats include:
- unauthorized reading/tracking,
- cloning or emulation,
- replay,
- relay,
- reader spoofing,
- tag spoofing,
- jamming/denial of service,
- malicious host-protocol input,
- authorization manipulation in the database.
13.3. Reader Security and Tag Security
A malicious reader extracting data from a legitimate tag is a different threat from a malicious tag deceiving a legitimate reader. A threat model should cover both directions.
13.4. Lightweight Cryptography
Passive tags can be constrained by power, memory, gate count, and execution time. This is why lightweight cryptography has been an important RFID research area.
“Lightweight” should not mean “weak.” Protocol design, key management, randomness, and side-channel resistance still matter.
RFID tags, smart cards, and general-purpose IoT nodes do not represent the same hardware class. A passive tag harvests energy from the reader's field, whereas a battery-powered IoT node may have a different processor, memory budget, and power envelope. Efficient AES execution on one target therefore does not establish equivalent performance on every tag or reader. Required confidentiality and authentication operations must fit the RF transaction timing budget and the device's capacity to protect secrets.
An implementation is assessed by code footprint (ROM), working memory (RAM), energy per authenticated message, end-to-end latency, and key-schedule cost. Freshness, message authentication, and resistance to key extraction are separate protocol requirements. Using only the AES block-cipher core does not prevent replay or unauthorized access. NIST SP 800-232 standardizes alternatives such as Ascon-AEAD128 for constrained platforms; it does not imply that every RFID tag can implement Ascon or that one primitive is universally optimal.
Meaningful comparisons use the same processor class, clock constraints, message lengths, security service, and assumptions about the key lifecycle. An optimization that reduces cycles but increases side-channel exposure may fail the security objective. The decision must account for both the primitive and the complete reader–tag–back-end trust chain.
13.5. Side Channels
Even a mathematically sound cipher can leak information through implementation behavior such as:
- timing,
- power consumption,
- electromagnetic emanations.
RFID devices are a good example of why hardware and software security cannot be designed independently.
13.6. Back-end Security
A secure tag cannot compensate for an insecure back end. Access-control systems still require:
- least privilege,
- strong administrator authentication,
- SQL-injection prevention,
- audit logging,
- secure network transport,
- secret/key management,
- controlled authorization changes.
The broader software-security perspective is covered in Secure Software Engineering.
13.7. Challenge-response Flow in RFID Authentication
A fixed RFID UID does not establish that a tag is genuine or unclonable. In challenge-response authentication, the reader generates a fresh nonce, the tag binds that nonce to context using a shared secret or a private key in a secure element, and the reader verifies the result within defined time bounds. Session-specific responses help resist replay, but key extraction, relay attacks, and weak randomness need separate controls.
Successful cryptographic authentication is not itself an access-grant decision: authorization, reader identity, location, time, and revocation must still be checked. Primitive and nonce selection are treated in Cryptology.
Unit 14: Reliability, Performance, and Debugging
14.1. Preserve Raw Evidence When Needed
If a card appears to be “read incorrectly,” storing only the normalized UID can hide the cause. Diagnostic records can include:
- raw bytes,
- parse result,
- port/reader identity,
- timestamp,
- protocol state,
- error code.
That makes it possible to separate parsing defects from hardware faults.
14.2. Timeout and Retry
Serial and network protocols require explicit:
- deadlines,
- timeouts,
- retry policies,
- cancellation behavior.
Retry safety depends on operation semantics. Retrying READ UID is not equivalent to retrying OPEN DOOR.
14.3. Latency and Throughput
An access system can care about both aggregate throughput and single-user response latency.
A useful decomposition is:
total latency = RF read + reader processing + host transfer + validation + DB + control outputOptimization should follow measurement of these components rather than guesswork.
14.4. Multiple Readers
Scaling from one to many readers introduces:
- connection lifecycle,
- concurrency,
- reader identity,
- duplicate events,
- time ordering,
- backpressure,
- fault isolation.
14.5. Layered Debugging and Fault Isolation
An RFID integration symptom may appear at the application layer while the actual defect is much lower. Verifying layers independently is faster and more deterministic than making speculative code changes.
A practical diagnostic order is:
- power, grounding, and physical connection,
- cable/pinout and electrical levels,
- operating-system visibility of the serial/USB device,
- raw byte/character stream,
- frame parser and checksum,
- identifier normalization,
- database and authorization query,
- application state and actuator command,
- physical feedback.
At each step, obtain an observation that is independent of at least one adjacent layer when possible. Correct raw frames in a terminal provide strong evidence about cable and serial configuration; correct authorization with no actuation shifts the investigation toward the physical-output boundary.
Unit 15: RFID, Databases, Networks, and IoT
15.1. Edge to Back End
A modern RFID deployment can be viewed as an edge-to-backend system.
The reader/gateway may:
- collect physical observations,
- filter or aggregate events,
- buffer locally,
- forward events to the back end.
The back end may:
- map identity,
- enforce authorization,
- preserve history,
- provide analytics,
- integrate with enterprise systems.
15.2. Network Failure
If readers are network connected, the design should decide:
- whether events can be lost,
- whether the reader buffers offline,
- whether reconnection causes duplicates,
- whether access decisions can be made locally.
At that point the RFID problem becomes a distributed-systems problem.
15.3. Database Design
RFID event streams coexist with relational identity and authorization data. Data modeling therefore involves:
- write rate,
- query patterns,
- indexes,
- retention,
- archival.
I cover the relational side in Database Management Systems and the network side in Computer Networks.
15.4. RFID and IoT
An RFID tag does not need to speak IP directly to participate in an IoT system. RFID often contributes physical identity and observations:
physical object
→ RFID identity/event
→ gateway/backend
→ digital state
Sensor-enabled RFID can extend this from identity into temperature or other measurements.
Unit 16: Software-defined Radio and Observing RFID
16.1. Why SDR Matters
Software-defined radio moves significant RF processing into programmable digital signal processing. For RFID research, this can help with:
- observing waveforms,
- modulation/demodulation experiments,
- protocol analysis,
- experimental reader implementations.
16.2. GNU Radio and USRP
GNU Radio can compose signal-processing blocks in software, while USRP-class hardware provides programmable RF sampling and transmission interfaces.
Software-defined radio addresses a different observation level from programming a commercial reader's host interface. In typical application integration the reader terminates the RF layer; SDR is a complementary laboratory instrument for observing waveform, spectrum, modulation, and timing closer to the physical layer.
16.3. Signals-and-systems Perspective
A deeper RF treatment requires concepts such as:
- spectrum,
- bandwidth,
- modulation,
- sampling,
- noise,
- filtering.
The mathematical basis is covered separately in Signals and Systems.
Unit 17: RFID Application Domains
17.1. Physical Access Control
In physical access control, the objective is not merely reading a card but producing a secure and traceable access decision from identity and authorization policy. Read event, authorization decision, door/turnstile command, and physical outcome should be recorded as distinct events.
17.2. Asset and Inventory Tracking
UHF RFID can identify large numbers of objects in warehouses, production, supply chains, and logistics. Reader placement, tag density, and item materials become significant design variables.
17.3. Libraries
RFID can support item identity, shelf workflows, and checkout/return operations. Metal shelving and high tag density can affect deployment behavior.
17.4. Healthcare
RFID can be used to relate medication, samples, devices, or patients. Here an incorrect association can become a patient-safety issue rather than only an inventory error.
17.5. Manufacturing
Tags on parts, pallets, or carriers can bind physical production flow to MES/ERP records. The value comes from synchronization between physical state and digital process state.
17.6. Transportation and Logistics
Container and vehicle tracking introduce outdoor operation, moving targets, large read zones, harsh environments, and multi-reader coordination.
Unit 18: Testing, Commissioning, and Verification
An RFID system is not verified merely because one card works on a laboratory bench. Commissioning should exercise the RF read zone, host protocol, data model, authorization, and physical actuator together.
18.1. Read-zone Mapping
Vary antenna placement and power while measuring successful reads inside the intended zone and unintended reads outside it, including the influence of metal and liquids. The goal is not maximum range but a predictable read zone.
18.2. Protocol Conformance and Raw Capture
Host integration should be tested with nominal traffic as well as fragmented frames, back-to-back frames, invalid checksums, unexpected lengths, timeouts, and disconnections. Raw traffic samples can become regression-test vectors.
18.3. Identifier and Data Consistency
The same credential should produce the same canonical identifier through different reader paths. Byte order, padding, hexadecimal case, and keyboard-wedge conversion require explicit test vectors.
18.4. Fault Injection
Controlled tests should remove reader power, interrupt serial/TCP connectivity, make the database temporarily unavailable, or suppress actuator feedback. Every case should produce an explicit failure state rather than silently recording uncertain physical state as success.
18.5. Acceptance Criteria
Acceptance should not be reduced to “the card was read.” Measurable criteria can include read success, unintended-read rate, decision latency, event loss, reconnect time, audit integrity, and physical behavior under failure.
This verification approach turns RFID from a device demonstration into an operable cyber-physical system.
Unit 19: Observability, Learning, and Anomaly Analysis
19.1. Read-zone Modeling and Observability
An RFID reader does not have a single spherical "range." Antenna gain, polarization, tag orientation, nearby metal or liquid, multipath, and reader power create an irregular three-dimensional read zone.
Validation should therefore measure repeated success/failure across position and orientation rather than a single "tag read" test. RSSI or phase can also be recorded where useful.
In access-control logic, a missed read is not equivalent to proof that a tag was absent. Application behavior must account for the physical probability of observation and anti-collision behavior.
19.2. Interpreting RFID Results with Physical Conditions
Reading a tag at one point is not proof of a fixed “range.” Antenna orientation, polarization, tag placement, nearby metal/liquid, reader power, and multipath all change read probability.
Installation tests should use repeated measurements across a position/orientation matrix rather than one pass. Read success, unintended adjacent-zone reads, and multi-tag anti-collision behavior should be observed together.
For security, UID and authentication are different concepts. Tag-family cryptographic capability, key management, and backend authorization are separate layers.
19.3. Learning and Anomaly Analysis in RFID Data
The AI connection in RFID appears primarily in the event data produced over time rather than in the reader itself. When tag identity, reader, antenna, time, and possibly signal strength accumulate at scale, pattern, anomaly, and estimation problems can be formulated. The model, however, inherits the limitations of the physical reading process.
A basic event can be viewed as:
(tag, reader, antenna, time, signal)Single events may be insufficient; windowed read counts, reader transitions, dwell time, or RSSI distributions can form features.
In a warehouse or production flow, unexpected reader sequences can be ranked as anomalies. Simple statistics, Markov models, or machine learning may be used. An anomaly is not automatically an error or malicious act; it is a deviation from a chosen reference behavior.
Learned methods can also assist entity resolution when deterministic identifiers are unavailable. If a stable EPC or card identifier already solves the identity problem, however, adding a learned matcher is unnecessary complexity.
RSSI- or phase-based localization is another possible application, but RF distributions are highly environment-dependent. Shelving, people, metal surfaces, and antenna placement can shift the data distribution, so cross-site generalization must be measured.
The raw-event chain should remain traceable:
RF condition
↓
read event
↓
window / feature
↓
model
↓
score
The model score does not replace the source observation. AI is justified where high-volume noisy event sequences contain patterns difficult to encode explicitly; it does not replace RFID's physical and protocol semantics.
19.4. Conclusion
An RFID system is not just a tag UID displayed on a screen.
The tag participates in the RF physical layer.
The reader converts that interaction into device-level data.
Serial, USB, or network transport carries the data to software.
A parser turns raw bytes into an event.
Normalization gives the identifier a canonical representation.
The database relates the tag to a person or asset.
Authorization decides whether an operation is permitted.
Logging makes the decision explainable later.
When an actuator is involved, the decision returns to the physical world.
The central systems-engineering lesson of RFID is that an event beginning in the RF domain should remain traceable through software, data modeling, authorization, and physical actuation. The same principle applies to more complex IoT and cyber-physical systems: a system is difficult to explain or trust when data cannot be traced from physical source to final effect.
Related Technical Notes
References
- Brendan Gregg. Systems Performance: Enterprise and the Cloud. Pearson Education, 2014.
- GS1. EPC Radio-Frequency Identity Generation-2 UHF RFID Standard.
- ISO/IEC 14443 series. Contactless proximity cards and devices.
- ISO/IEC 15693 series. Contactless vicinity objects/cards.
- ISO/IEC 18000 series. RFID air interfaces for item management.
- Klaus Finkenzeller. RFID Handbook, 3rd ed. Wiley, 2010.
- Mor Harchol-Balter. Performance Modeling and Design of Computer Systems: Queueing Theory in Action. Cambridge University Press, 2013.
- Xinxin Fan (Ed.). Radio-Frequency Identification (RFID): Emerging Technologies, Applications and Improvement Strategies. Nova Science Publishers, 2014.
- NIST. SP 800-232: Ascon-Based Lightweight Cryptography Standards for Constrained Devices, 2025. https://csrc.nist.gov/pubs/sp/800/232/final
- NIST. SP 800-38D: GCM and GMAC, 2007. https://csrc.nist.gov/pubs/sp/800/38/d/final