


Digital Forensics Engineering

An engineering-oriented course covering the digital-evidence life cycle from first response and forensic acquisition to file systems, memory, network, mobile and cloud analysis, tool validation, correlation, and reporting.
Digital forensics engineering is not merely the act of “finding data” after an incident. Its objective is to establish a repeatable engineering process for identifying, preserving, acquiring, examining, analyzing, interpreting, and reporting potential digital evidence. A technically interesting artifact is not automatically strong evidence. Provenance, acquisition method, transformations applied to the data, and the ability of an independent examiner to reproduce the result are as important as the finding itself.
This course treats first response, forensic acquisition, hashing, file-system and deleted-data analysis, network and memory forensics, mobile devices, cloud evidence, timeline reconstruction, tool validation, and technical reporting as one evidence lifecycle. Its final two units address the expert witness's scope of authority and the preparation of an official expert-witness report. Legal authority, procedure, and admissibility vary by jurisdiction. This course does not provide legal opinions; technical methods must be applied within authorized procedures and institutional rules. For adjacent topics, see Information Technology Law, HTS Analysis, and Cybersecurity Engineering.
Unit 1: Digital Evidence and the Engineering Foundation
1.1. The Evidence Lifecycle
A useful high-level model is:
preparation
  ↓
identification
  ↓
preservation
  ↓
acquisition
  ↓
examination
  ↓
analysis and interpretation
  ↓
reporting
  ↓
independent review / reproduction
The sequence is not a one-way pipeline. Analysis may reveal a previously unknown source that requires another acquisition. Every stage should therefore record its inputs, outputs, assumptions, and side effects.
1.2. Digital Evidence Integrity and Volatility
Digital data can be copied with extraordinary fidelity, but it can also be modified by ordinary system behavior. Mounting a disk read-write, opening an application, synchronizing a mobile device, installing an acquisition agent, or allowing a cloud log to age beyond its retention period can change what remains available.
The correct preservation question is therefore not simply “did anyone touch the device?” It is: which action can modify which evidence, and is that modification justified and documented?
1.3. States of Data
Evidence can be considered in three broad states:
- Data at rest: persistent storage on disks, SSDs, removable media, and service storage.
- Data in use: RAM, running processes, open handles, decrypted keys, session tokens, and live application state.
- Data in transit: packets, flows, messages, and protocol transactions moving through a network.
The state affects acquisition. A powered-off disk may permit bit-level imaging, while a full-disk-encryption key that exists only in memory may disappear when power is removed.
Unit 2: First Response, Scene Handling, and Secure Transport
First-response decisions at a digital scene consider device power state, network connectivity, and risk of volatile-data loss. Because each intervention may alter evidence, record the initial state and rationale before acting. Compare isolation, shutdown, and live acquisition in context rather than imposing one universal sequence. Preserve who acted, when, with which tool, and with what observed result for later review.
2.1. The Goal of First Response
First response should stabilize the situation and preserve future investigative options rather than immediately perform deep analysis. Personnel safety, legal authority, physical security, device state, network state, and likely evidence sources must be considered together.
Preparation should include more than a tool kit:
- scope and authority,
- team roles,
- expected device and network types,
- estimated data volume,
- clean target storage,
- power and interface adapters,
- write blockers,
- synchronized clocks and documentation forms,
- transport and physical protection,
- special risks such as encryption, remote wipe, anti-forensics, or hazardous environments.
2.2. Initial Response Decisions for Powered-On and Powered-Off Devices
There is no universal rule that says “always shut it down” or “never shut it down.” Volatile data value, encryption, remote-access risk, malware behavior, open sessions, and organizational procedure determine the decision.
Any live response changes state. Commands consume memory, tools create processes, logs advance, and caches evolve. When live acquisition is justified, the examiner should record commands, tool versions, timestamps, and known side effects. Current SWGDE guidance similarly emphasizes least-invasive live collection and explicit documentation of changes created by the collection itself.
2.3. Order of Volatility
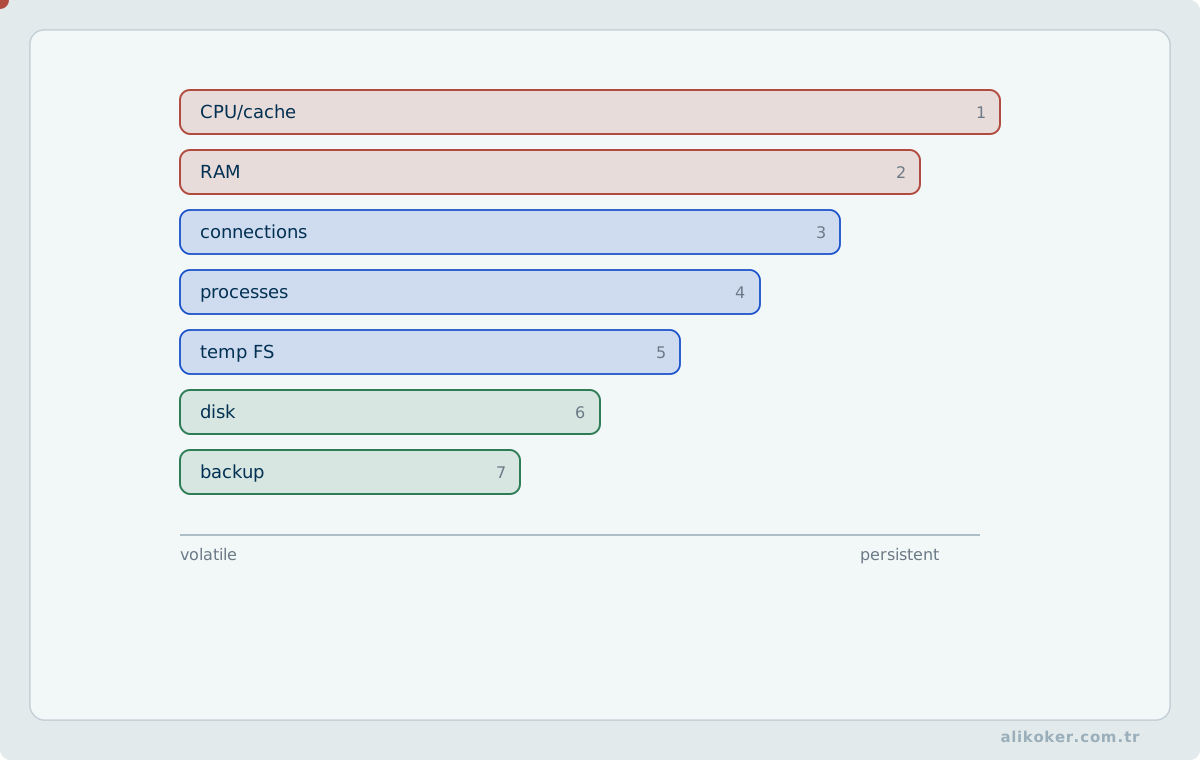
Different sources disappear at different rates. A conceptual order is:
processor / transient execution state
        ↓
RAM, processes, active connections
        ↓
temporary files and live logs
        ↓
persistent file systems
        ↓
backups and remote copies
This is not an absolute recipe. A remotely retained cloud log can be more perishable than a local disk. Priority follows the incident-specific risk of loss.
2.4. Modeling the Technical Scene
A digital scene is not limited to a physical room. A desktop, wireless access point, network storage system, printer queue, mobile device, online account, and remote service can all be evidence surfaces of the same event. The goal of first response is therefore not to seize the largest possible number of devices, but to determine which systems generate which evidence sources and how those sources relate to one another.
Before deployment, a technical response plan should answer at least the following questions:
- What device classes and approximate data volumes are expected?
- Which systems are likely to be powered on?
- Is there a risk from encryption, remote wiping, synchronization, or central management?
- What is known about network topology, server roles, and responsible technical personnel?
- Which adapters, write blockers, power supplies, or special interfaces may be required?
- Which evidence sources are volatile enough to deserve priority?
- Is there sufficient capacity for secure transport and temporary storage?
Preparation also means validating the tools before they reach the scene. A tool being installed is not enough; its version, configuration, time source, licensing state, and output format should be known.
2.5. Scene Security and Documentation
Context loss is as serious for digital evidence as it is for physical evidence. Before equipment is moved, responders should document screen state, cabling, open applications, attached peripherals, serial numbers, network connections, and visible error messages. Photographs, video, diagrams, and evidence labels serve different purposes and should be used together.
A photograph of a device by itself may be insufficient. The relationship between an external drive and a particular USB port, or between a switch port and a particular cable, can later become important for ownership and timeline questions. Documentation should preserve a chain such as:
physical location
    -> device identity
        -> connection/port
            -> logical source
                -> acquired forensic image
2.6. Decision Model for Live Systems
Powered-on versus powered-off handling is a central first-response decision. Modern systems make that choice especially consequential: full-disk encryption, keys in RAM, authentication tokens, ephemeral containers, and active cloud sessions can disappear at shutdown. At the same time, every command executed on a live host changes its state.
There is therefore no universal rule that a live system should always be powered off or always examined live. The decision depends on:
- the value of volatile evidence,
- system criticality,
- encryption state,
- risk of remote action,
- active malicious processes,
- legal and organizational authority,
- side effects of the collection tool,
- operational impact of interruption.
Live collection should record the expected side effects of each action. Capturing memory changes memory; enumerating network connections invokes system functions and may create logs. This does not invalidate the method. The relevant requirement is that the change be predictable, bounded, and documented.
2.7. Order of Volatility and Acquisition Priority
Order of volatility should not be memorized as simply “RAM before disk.” Different sources decay at different rates:
CPU/register/cache state
        ↓
running processes and RAM
        ↓
network sessions / ARP / routing / socket state
        ↓
temporary files and buffered logs
        ↓
local persistent storage
        ↓
remote logs / backups / archives
The incident can change this priority. During a network intrusion, short-lived connection state may be more valuable than disk imaging. On a physically failing storage device, repeated power cycles can reduce the chance of successful recovery.
2.8. First Response by Device Class
2.8.1. Desktops and Laptops
Power state, screen contents, attached storage, network connections, and active sessions should be documented. A powered-off device is not booted merely for convenience. A live device should not be powered down until encryption and volatile-evidence needs have been evaluated. External storage should receive an independent evidence identity.
2.8.2. Servers
Server intervention can have a much larger operational effect than work on a single-user computer. Virtual machines, containers, shared storage, RAID, centralized logging, and concurrent user sessions are separate sources. Removing a physical disk is not always the correct acquisition method; service availability and consistency must be considered.
2.8.3. Network Devices
Routers, switches, firewalls, and wireless access points can maintain running state that differs from persistent configuration. ARP caches, NAT tables, connection tables, DHCP state, clock/NTP status, and short-lived log buffers may disappear after shutdown. A configuration backup alone does not describe an active incident.
2.8.4. Printers, Scanners, Copiers, and Similar Systems
Multifunction devices can hold print jobs, address books, authentication information, scan destinations, local storage, and network logs. They should not be ignored simply because they are categorized as peripherals.
2.8.5. Portable and Embedded Systems
Cameras, navigation devices, media players, smart watches, IoT devices, and industrial controllers may require methods that differ from desktop forensics. Serial/JTAG access, storage removal, or vendor-specific protocols may be necessary. Because hardware intervention can be irreversible, lower-impact methods should be evaluated first.
2.9. Packaging, Transport, and Environmental Risk
Antistatic protection, impact resistance, and radio-frequency shielding serve one underlying principle: transport must not introduce a new physical or logical effect. Mechanical shock, electrostatic discharge, moisture, extreme temperature, and unauthorized wireless communication are different threat classes.
A Faraday bag is not a universal solution for mobile devices. Loss of signal can increase power consumption, heat, and battery depletion. Modern devices also expose multiple radios such as cellular, Wi-Fi, Bluetooth, NFC, and eSIM-associated functions. Isolation should be validated for the device and situation.
2.10. Faraday Cages and Radio Isolation of Mobile Evidence
An unisolated mobile device can continue to receive remote commands, synchronize data, or generate new communication records before examination. Radio isolation requires evaluating different options, including a shielded enclosure, airplane mode, and powering the device down. These choices are not equivalent. Power-off can destroy volatile state, introduce authentication barriers after restart, or alter access to encrypted material; leaving the device on can sustain background processing and battery consumption.
A Faraday bag or box may attenuate cellular, Wi-Fi, Bluetooth, and other radio paths over specified frequency ranges and conditions; complete blocking must not be assumed. Seams, poor closure, inserted cables, or incorrect use can allow communication. Continued network searching can increase battery drain. NIST SP 800-101 Revision 1 explicitly addresses these trade-offs and the possibility of incomplete attenuation in Faraday enclosures.
The initial-response record should cover current power and lock state, battery level, volatile evidence, authority for acquisition, and potentially irreversible interactions. Successful radio isolation does not freeze all device data or establish hash-based evidentiary integrity. It is one layer of the forensic acquisition process.
2.11. Validation and Documentation of Radio Isolation
Validation of isolation cannot be reduced to the signal icon on the device display. Supported radios, operating frequencies, ambient field level, device location within the enclosure, and physical enclosure condition define the test context. One failed test call does not prove all radio services are disabled; a short successful test does not establish continuous isolation throughout examination.
The evidence record should identify the enclosure, pre-use physical inspection, insertion time, cable and power connections, test method, observed outcome, and uncertainties. Data may already have been altered by remote synchronization before isolation. Changes to local time records, running processes, or battery status during isolation must also be recorded where relevant.
No universal shielding pass/fail number applies to every forensic device. Acceptance criteria depend on the threat model, relevant frequency bands, and test configuration. Electromagnetic fundamentals belong in Electronics I and II; this section concerns the evidentiary consequences of intervention.
2.12. Initial Acquisition of Audio and Video Records
When transferring files from recorders, document source storage, file systems, containers, codecs, time fields and channel arrangement. For analogue tape, additionally document playback speed, playback equipment condition and digitization chain. Do not replace the first acquired sample with enhanced audio or video.
For video, examine clock settings, local-time offsets and variable frame rates. When aligning audio and video, retain the time markers and alignment parameters used for correspondence.
Unit 3: Evidence Identity, Chain of Custody, and Integrity
Evidence-integrity verification starts by documenting identity and acquisition conditions. Compare cryptographic digests at appropriate points before and after transfer, while recognizing that matching digests alone do not establish legal provenance. Log storage, access, and transformation separately. Keep analytical derivatives distinct from originals and document transformations so findings can be reproduced.
3.1. Evidence Identity
An evidence item should be traceable through information such as:
evidence identifier
source device / account / service
serial number or logical identifier
collector
acquisition time and time zone
location
acquisition method
tool and version
output files
hash values
subsequent transfers
Chain of custody is not merely a signed form. It is the continuous record of who possessed the evidence, when, for what purpose, and in what condition.
3.2. Hash-Based Integrity Evidence and Its Limitations
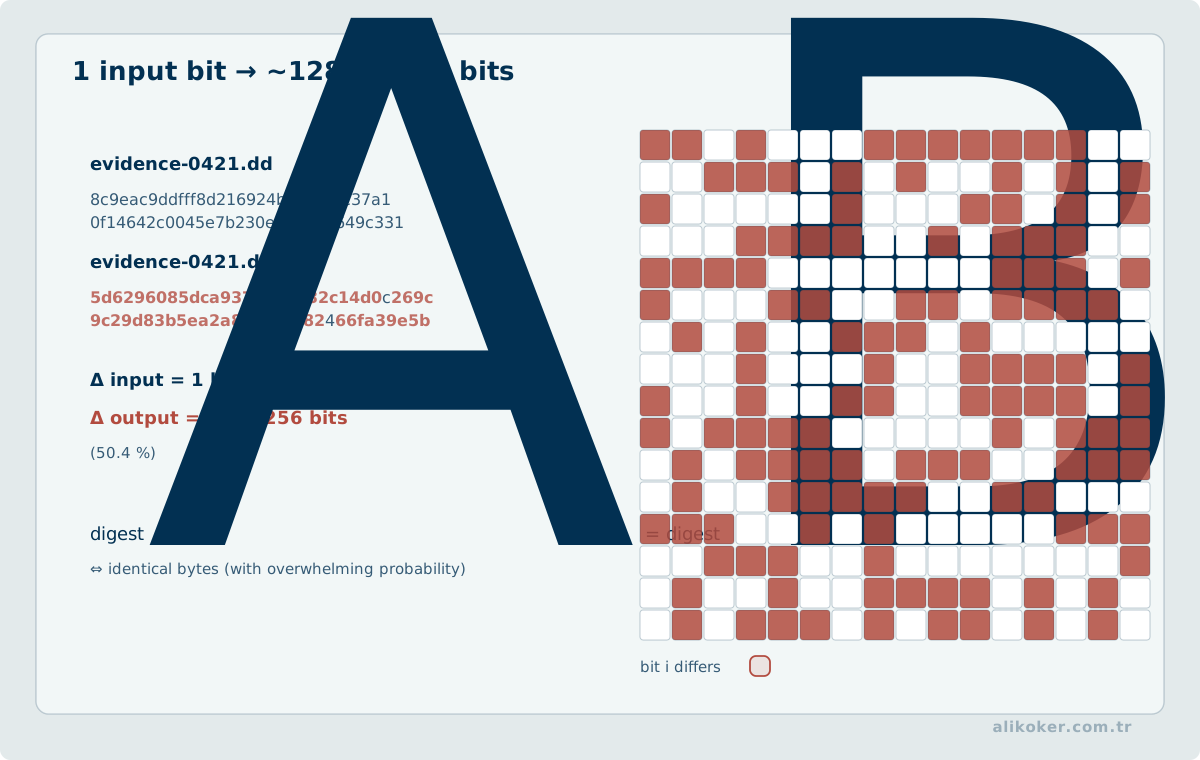
A cryptographic hash is a digest of a particular byte sequence. It is therefore useful for demonstrating that a forensic copy still contains the same bytes as the acquired source representation.
source bytes --hash--> H1
copy bytes   --hash--> H2
H1 == H2  -> strong bit-level integrity check
A hash is not the same as a digital signature. A digital signature binds integrity to a private-key operation and an identity context; a hash alone only summarizes data. It also does not prove who created a file or whether the represented event is legally authentic.
MD5 and SHA-1 were historically common in forensic workflows, but their collision resistance is no longer suitable for new cryptographic designs. SHA-256 or another current digest should normally be preferred. Historical evidence carrying MD5 values is not automatically invalid; the overall validation context and any additional hashes matter.
Placing evidence verification at processing boundaries. After acquiring a disk image, compute integrity digest H₀ and record it with the evidence identifier, acquisition time, source, and procedure. For a working copy representing the same bit sequence, digest H₁ is expected to satisfy H₁ = H₀. If files are extracted, archives unpacked, or content normalized, the derived object receives its own identifier and digest; a transformed artifact is not expected to hash identically to the original image. Processing records retain links between input and output objects. Equality of two digests alone does not establish legal admissibility, acquisition-tool correctness, or reliable timestamps; it only contributes evidence of integrity for specified data objects. Findings must clearly distinguish original evidence, derived data, and interpretation.
3.3. Evidence Digests, Chain of Custody, and Verification Model
A SHA-256 digest of a forensic image is a comparison value for a precisely defined byte sequence. Matching acquisition and pre-analysis digests supports integrity but does not, on its own, prove the original source or rule out acquisition error. Record device identity, acquisition time, tool version, write-protection state, scope, and operator separately. For large datasets, chunk hashes can be assembled into a Merkle tree, allowing efficient membership verification against a trusted root.
Do not confuse deprecation of a cryptographic algorithm with the need to preserve historical evidence records. An MD5 value in an old record may remain as provenance, while a modern collision-resistance claim requires a stronger additional digest. Cryptology explains the mathematical difference between hashes and signatures; legal admissibility depends on evidence beyond digest equality.
3.4. Distinguishing Electromagnetic Protection from Evidence Integrity
Electromagnetic shielding attenuates a physical communication path; evidentiary integrity requires traceable and verifiable records that acquired digital information has not been improperly altered. An operating system may continue running inside a Faraday enclosure, advancing timestamps and changing caches. Treating radio isolation as equivalent to hashing, write blocking, or chain of custody is therefore a methodological error.
Where appropriate, verification involves the pre- and post-acquisition action log, device state, tool version, output identity, and hashes of suitable acquired artifacts. A changing memory image is not necessarily expected to preserve the same hash during radio isolation. Differences should be attributed separately to device activity, acquisition decisions, or transformations by analysis tools.
Two distinct sets of acceptance criteria are needed: radio-connectivity and shielding tests on one hand; acquisition reproducibility, provenance, and integrity checks on the other. Success in one cannot substitute for evidence in the other.
Unit 4: Forensic Acquisition, Imaging, and Write Protection
4.1. Physical and Logical Acquisition
Physical acquisition attempts to capture raw storage at a lower level and may expose unallocated space, deleted content, and file-system structures.
Logical acquisition obtains objects exposed by a file system, application, operating system, or service API. For modern mobile platforms, SaaS systems, and cloud environments, logical acquisition may be the only practical and authorized method.
physical acquisition -> broader raw representation
logical acquisition  -> richer semantic context
Neither is universally superior. Encryption, device state, access method, storage technology, and investigative objective determine fitness for purpose.
4.2. Write Protection
A write blocker reduces the risk of accidental writes to source media. It is an important control, but the presence of a device does not by itself validate the workflow. Interface type, bridge hardware, operating-system behavior, source technology, and tool version should be tested and documented.
SSDs complicate assumptions inherited from magnetic disks. Controller firmware, TRIM, garbage collection, and wear leveling can make the physical persistence of deleted data unpredictable.
4.3. Forensic Images
A defensible acquisition record should include:
- source description,
- start and completion time,
- read errors and retries,
- acquisition extent,
- output format,
- tool version and settings,
- hash values,
- operator notes.
Forensic containers such as E01 or AFF4 can carry metadata and segmentation; raw images are simpler. Format selection should be driven by interoperability, validation, compression, integrity, and long-term accessibility rather than habit.
4.4. Evidence Acquisition Strategies
“Forensic imaging” describes a family of acquisition strategies rather than one operation:
- Physical acquisition: capture of the widest feasible addressable storage space.
- Logical acquisition: collection of objects exposed by a file system, application, or supported API.
- File-system acquisition: collection that preserves directory structure, metadata, and files.
- Targeted acquisition: selective acquisition under time, volume, or authority constraints.
Targeted acquisition is efficient but can be incomplete if a new question emerges later. Physical acquisition may provide a broader evidence surface, but it is not always feasible on modern mobile platforms with hardware-backed encryption and secure execution environments.
4.5. Sector-Level, File-Level, and Content-Targeted Copies
Block-level acquisition can preserve unallocated space and remnants that are invisible to the active file system. File-level acquisition can be entirely appropriate when only live files and metadata are required, but it limits deleted-data analysis. The method should follow the investigative question:
question: is deleted/unallocated data relevant?
        |
       yes -> prefer block/physical acquisition where feasible
        |
        no -> logical acquisition may be sufficient
4.6. Engineering Meaning of Write Protection
A write blocker is not simply a box placed between a drive and a workstation. The trust boundary lies between source media and the examination environment. Hardware write blockers provide a common, testable control; software-based blocking requires greater trust in the operating system, driver stack, and configuration.
A write-protection method should be tested for:
- correct device recognition,
- successful read operations,
- rejection of write commands,
- reporting of blocked or failed operations,
- support for the storage interface in use.
SATA, SAS, NVMe, USB, UFS, and embedded interfaces do not necessarily share the same blocking mechanism.
4.7. Image Formats and Acquisition Logs
Raw images (raw/dd) provide a simple representation. E01/EWF-style forensic containers can add segmentation, compression, metadata, and integrity information. Format choice should consider tool validation, interoperability, storage cost, and the downstream examination chain.
An acquisition log should record at least:
- source and destination identity,
- serial number and capacity,
- interface and write-protection method,
- tool and version,
- start and end times,
- time zone,
- read errors and bad sectors,
- source/output hashes,
- operator and evidence number.
4.8. Read Errors and Damaged Media
On damaged media, repeated attempts can make recovery worse. Physical condition should be assessed first. Mechanical disks showing abnormal sound, electronics damage, or surface failure may require specialized recovery and clean-room procedures. Aggressive retry policies can further stress marginal media.
The acquisition tool should record unreadable sectors, retry policy, and skipped regions. A successful output hash does not prove that the original source was fully readable; it proves that the resulting byte sequence has a stable identity after acquisition.
4.9. Hashing, Verification, and Evidence Identity
A hash value does not carry the entire evidential meaning of an item. Two verification questions should be separated:
- Acquisition verification: whether the output corresponds to the source that was intended to be acquired.
- Preservation verification: whether an already acquired object has changed since its hash was recorded.
SHA-256 and other current cryptographic hash functions are preferred for modern workflows. MD5 and SHA-1 remain visible in legacy tools and case formats; they should not be selected as the sole security mechanism for a new design. Multiple hashes can be retained when interoperability with historical tooling requires them.
Unit 5: Storage Media, File Systems, Deleted Data, and Timelines
5.1. Content and Metadata
A file is more than its payload. File systems may provide:
- name and path,
- inode/MFT-like records,
- size,
- permissions,
- creation/modification/access timestamps,
- allocation state,
- alternate streams or extended attributes.
Deletion often removes metadata references before every underlying byte is overwritten. However, SSD behavior and TRIM make the old claim that deleted data is always recoverable increasingly unreliable.
5.2. File Carving
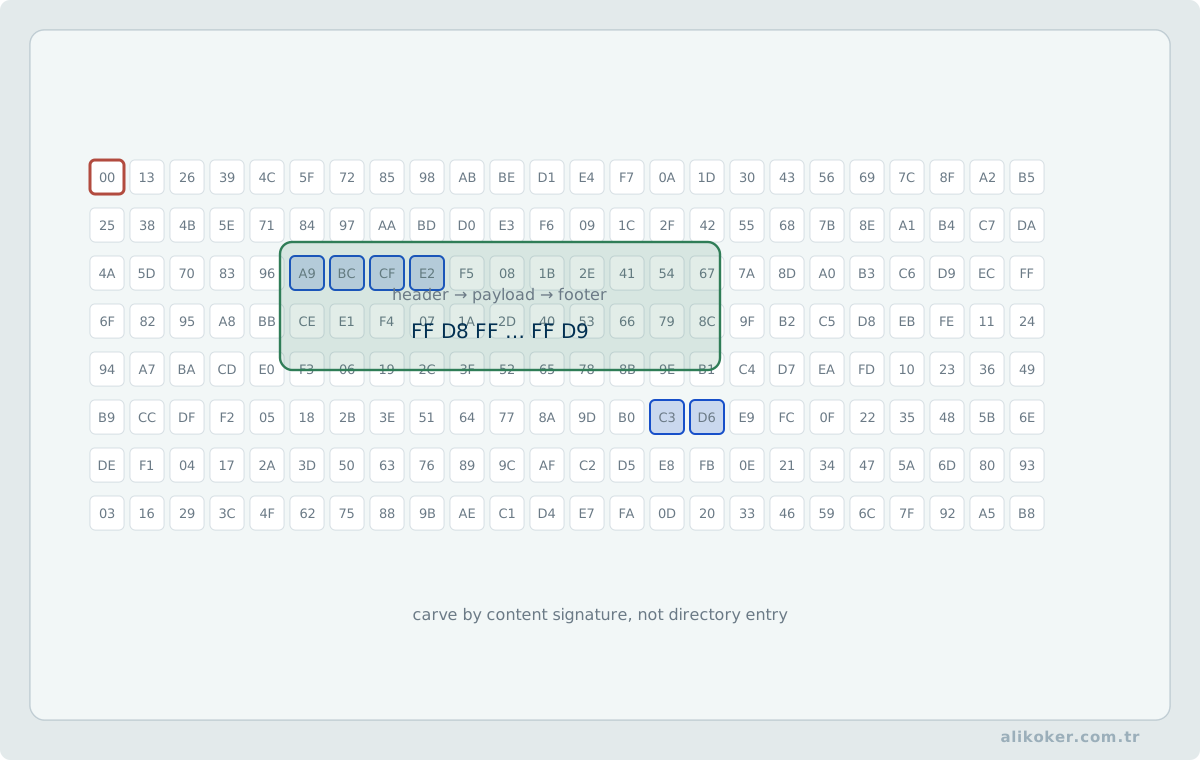
When file-system metadata is absent, carving searches raw data using file signatures and structural rules. See Digital Forensic File Carving Algorithms for a deeper treatment.
A carved object does not have the same provenance as a normal file-system record. Fragmentation, false positives, truncated objects, and internal-format validation must be considered.
5.3. Timeline Reconstruction
A reliable timeline should combine independent sources:
file-system timestamps
+ operating-system logs
+ browser history
+ application data
+ network records
+ identity-provider events
+ remote-service logs
= correlated timeline
Time zones, daylight-saving rules, clock skew, NTP adjustments, virtual-machine snapshots, and manually changed clocks can all alter interpretation. A timestamp is an observation; chronology is an inference built from multiple sources.
5.4. Storage Media and File-System Engineering
The meaning of digital evidence does not come from file contents alone. The behavior of the storage medium, partition layout, file system, controller layer, and operating system determines how much historical data can remain and how timestamps should be interpreted. A forensic examiner should therefore ask not only “what is on the disk?” but also “how does this system place, modify, and delete data?”
5.5. HDDs, SSDs, and Removable Media
Magnetic disks provide a relatively stable logical view of sectors, although remapping, error correction, controller caches, and firmware still abstract the physical medium. SSDs introduce a much stronger abstraction. Flash Translation Layers, wear leveling, garbage collection, and TRIM mean that a logical block address exposed to the operating system does not map permanently to one NAND location.
That distinction changes expectations around deleted data. On a magnetic disk, directory metadata may be removed while content remains until overwritten. On an SSD, TRIM and later garbage collection can make the same assumption unreliable. Neither “deleted files are always recoverable” nor “TRIM means nothing can ever be recovered” is a sound rule. Controller behavior, operating system, file system, interface, encryption, and elapsed time all matter.
USB storage, memory cards, optical media, and external enclosures also add interface layers. USB-to-SATA bridges, card readers, and hardware-encryption enclosures may hide device geometry or health information. The acquisition method must expose enough of the underlying device for the forensic objective.
5.6. Separating Partition, Volume, and File-System Layers
A physical medium may contain several abstraction layers:
physical device
  -> partition scheme
      -> partition / logical volume
          -> file system
              -> file / directory / metadata
                  -> application artifact
Partition metadata such as MBR/GPT is not the same thing as NTFS, FAT/exFAT, ext-family, or other file-system metadata. Even when a forensic suite hides these details, the examiner must know which layer produced a finding.
5.7. Unallocated Space, Slack, and File-System Metadata
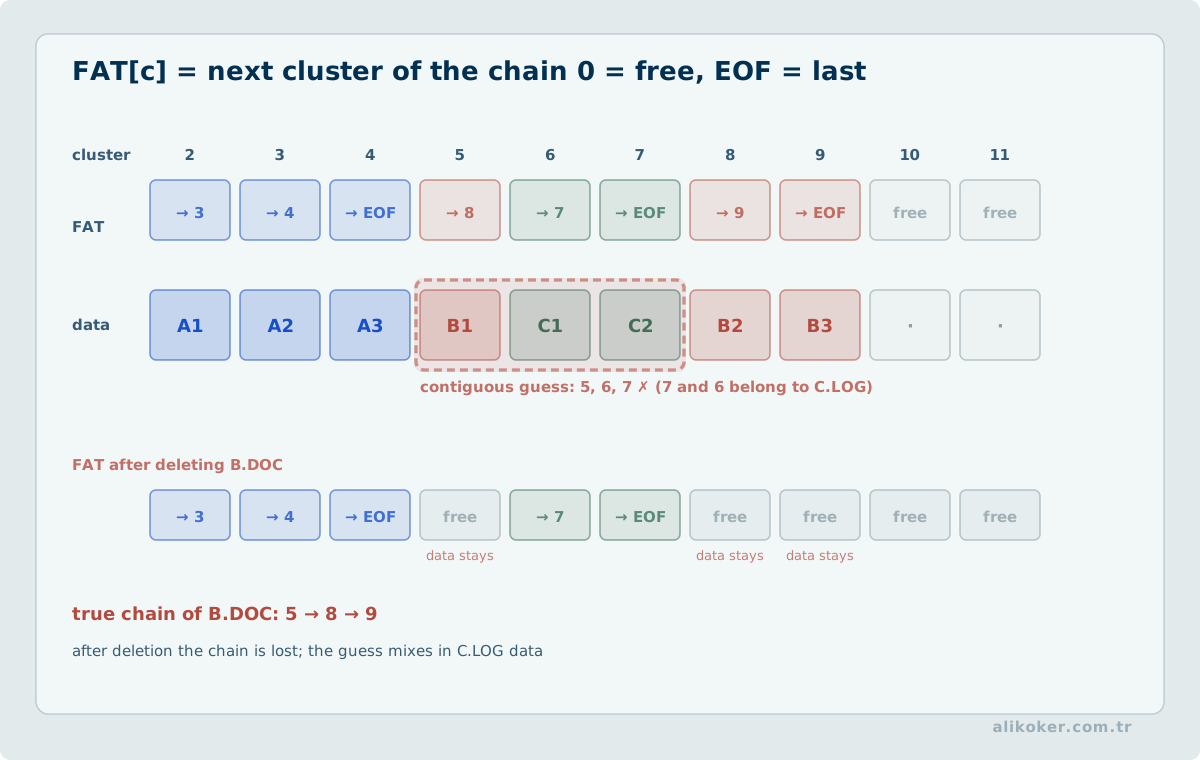
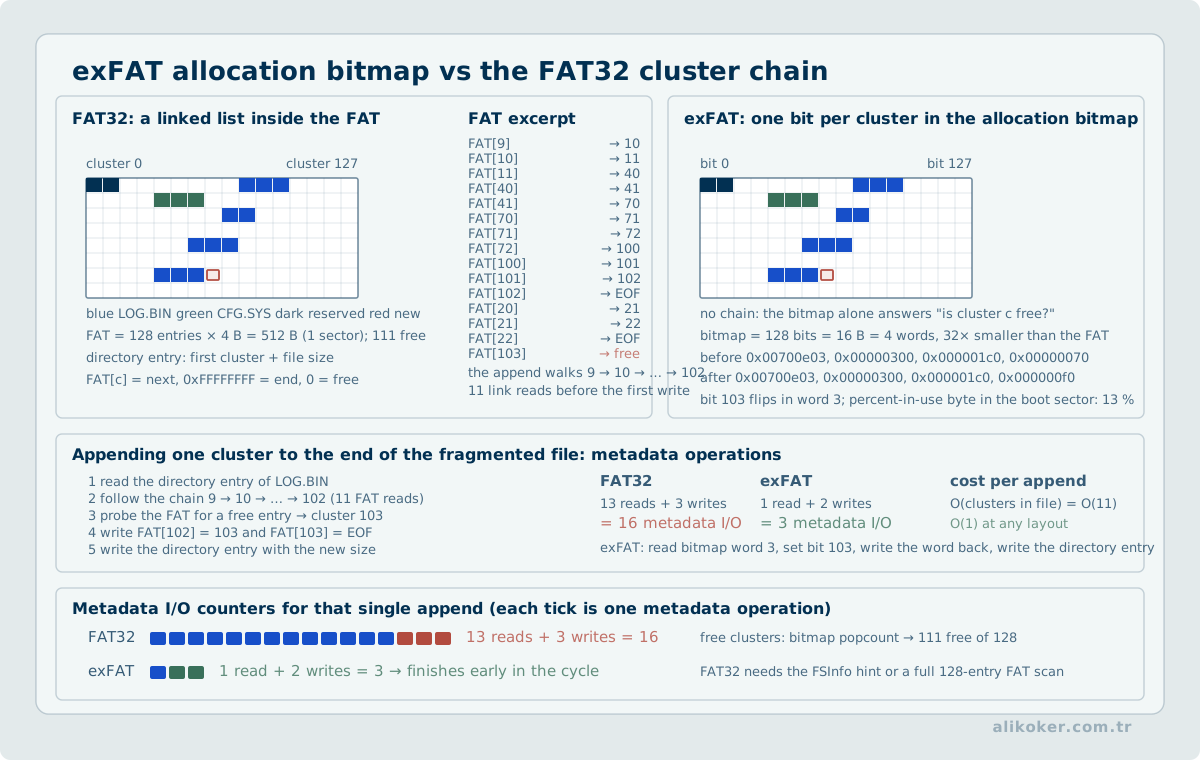
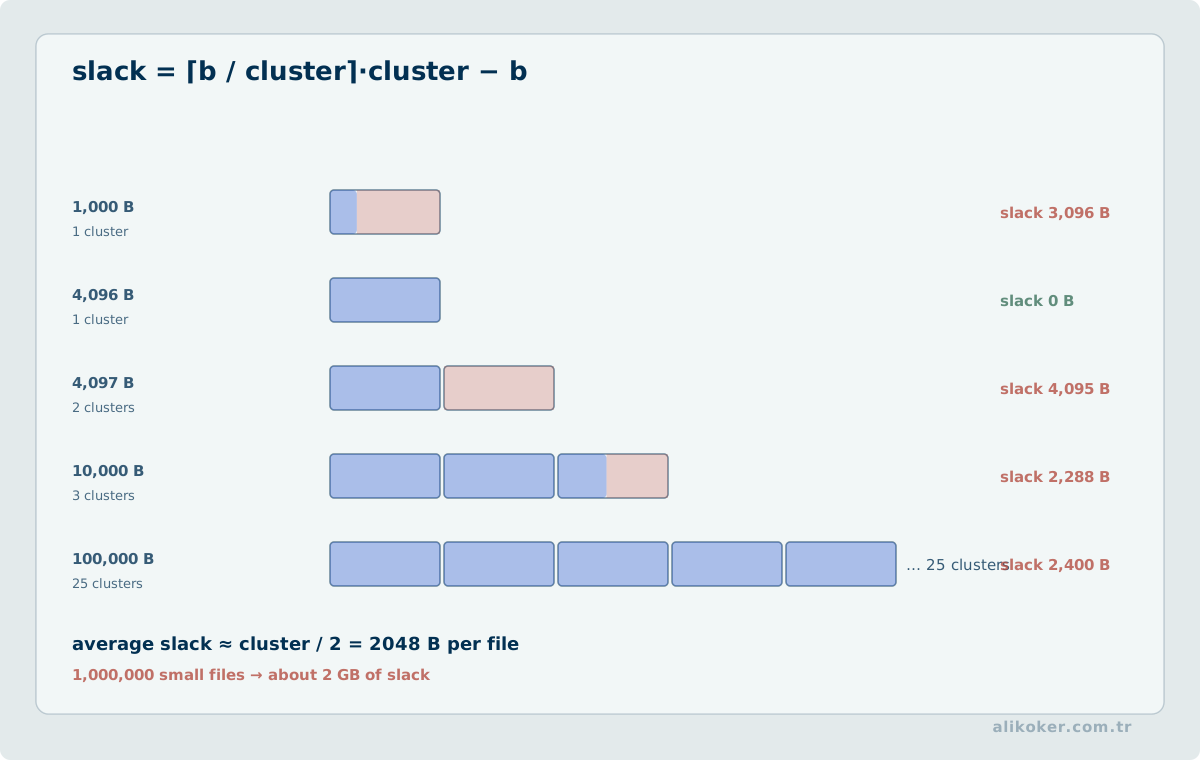
Space not allocated to active files may retain fragments of earlier content. Cluster or file slack can exist where allocated storage exceeds logical file length. Modern file systems complicate this simple model with compression, sparse files, copy-on-write, journaling, snapshots, and other allocation strategies.
Metadata is more than a filename and a timestamp. File identifiers, parent relationships, permissions, alternate streams, journals, extended attributes, and transaction records can contribute to event reconstruction. Timestamp semantics are file-system-specific; two fields both labeled “modified” do not necessarily represent the same event.
5.8. Journaling and Copy-on-Write Effects
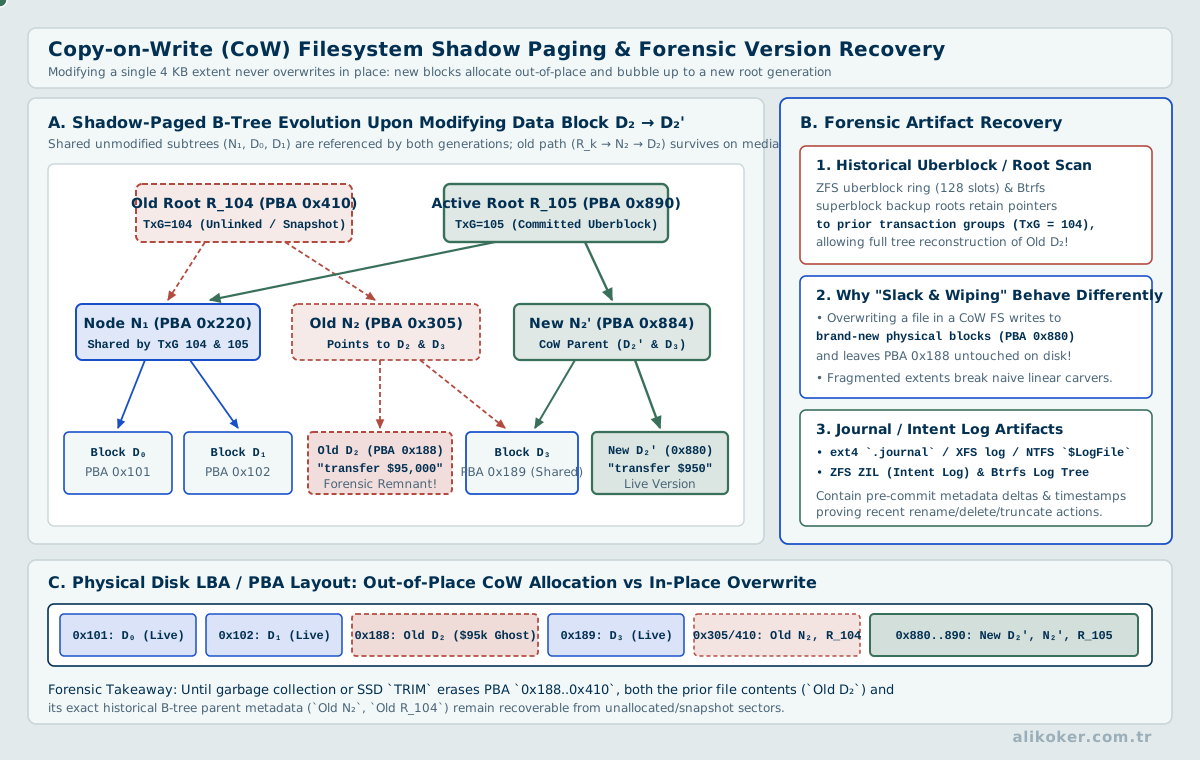
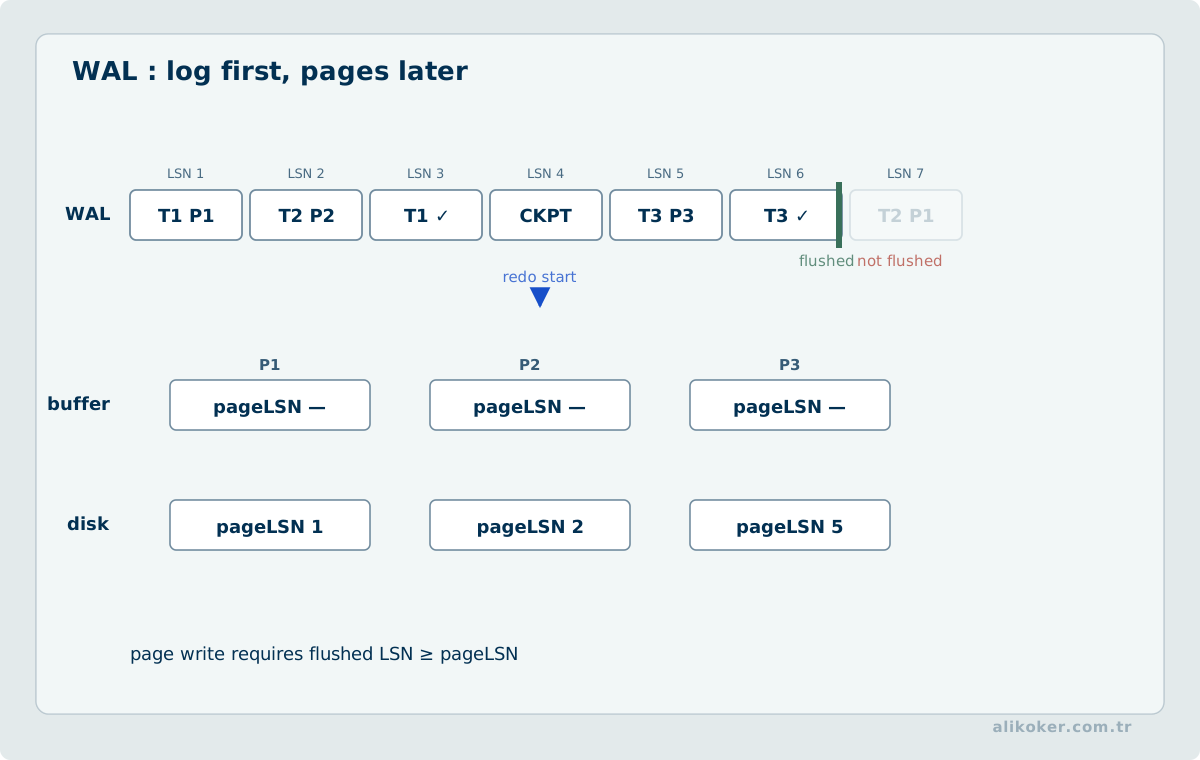
Journaling file systems record metadata, and sometimes data changes, to improve consistency. Those records can expose traces of earlier operations, but a journal entry by itself does not prove a specific user action. Copy-on-write and snapshot mechanisms can likewise preserve historical states that are invisible in the active namespace.
5.9. RAID, NAS, and SAN Environments
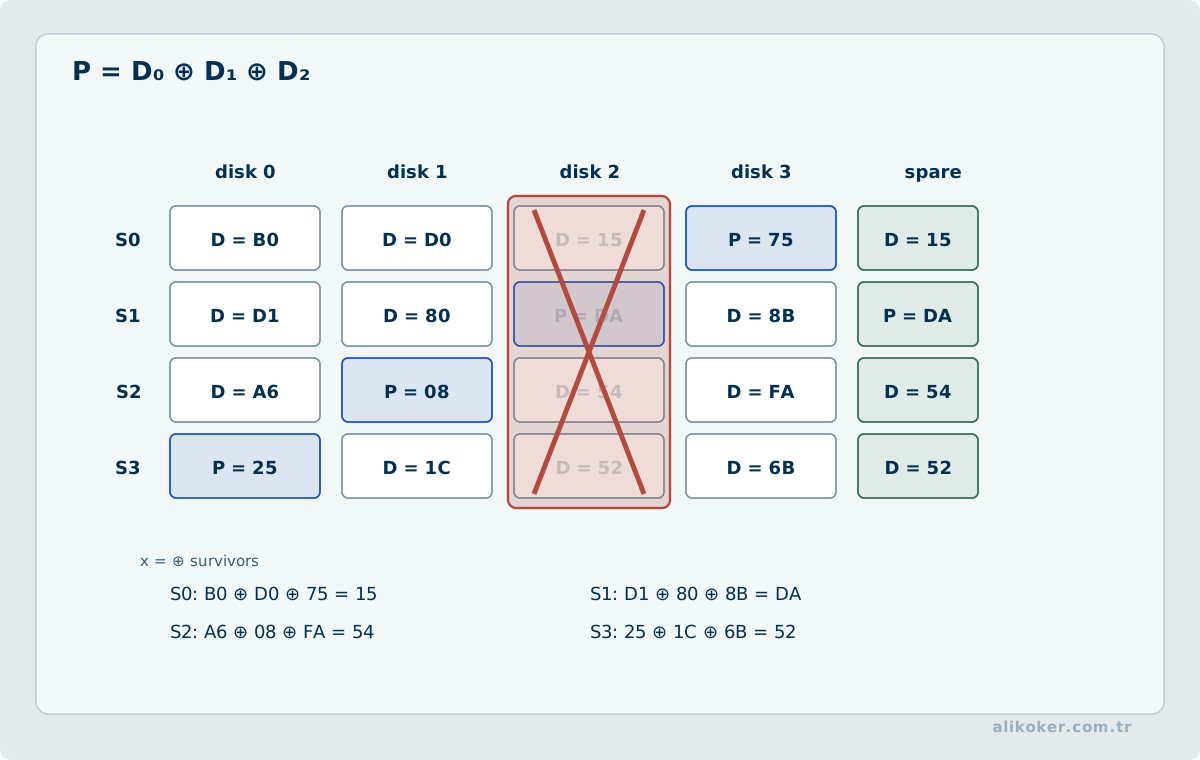
RAID and networked storage require separate acquisition reasoning. In such environments, imaging one disk is often insufficient. RAID level, member order, stripe size, parity layout, controller metadata, and missing members affect reconstruction.
one member-disk image
   !=
forensic view of the RAID logical volume
A NAS appliance can expose evidence in its operating system, account database, protocol logs, and snapshots as well as its disks. In a SAN, LUN mapping, storage-network events, and the host file system are separate layers. When a live service cannot be stopped, storage snapshots may be appropriate, but their consistency guarantees and creation time must be documented.
5.10. File Signature versus Extension
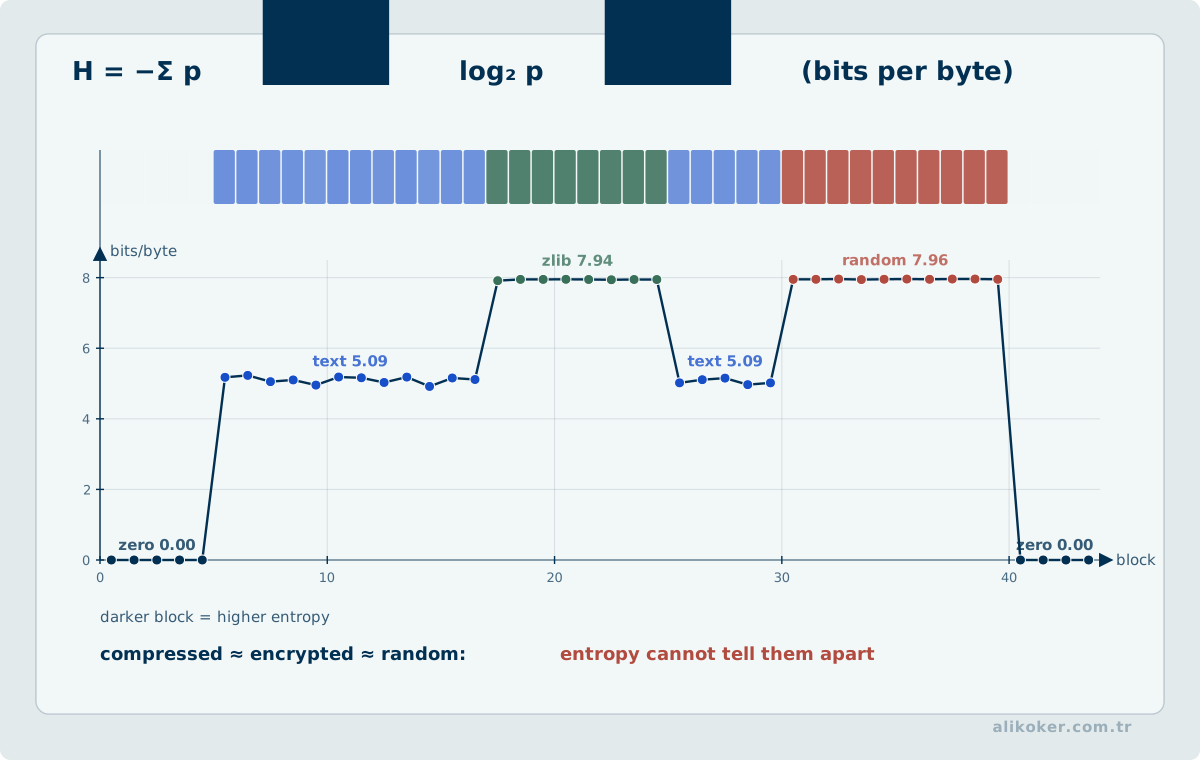
A filename extension is user-interface metadata, not proof of a file format. Magic bytes, structural validation, and content parsing can be combined. Looking only at a few initial bytes is also insufficient because polyglot files, embedded content, and damaged headers can mislead simple classifiers.
A stronger analysis model is:
extension -> initial hypothesis
signature/structure -> format validation
parser -> semantic interpretation
context -> evidential meaning
5.11. Temporal Relations and Reproducibility in Digital Forensics
In temporal networks, when an edge occurs is part of the structure, not merely metadata. In a forensic event graph, removing time and producing one static network can make events separated by days appear to belong to the same causal chain, while short-lived interactions close to the incident can be masked by high-volume routine relationships. Time-respecting paths, temporal reachability, edge persistence, burstiness, and time-dependent centrality therefore complement static degree and one-shot community partitions.
- Analyze events through time-respecting relation chains rather than shared nodes alone.
- Record the effect of clock skew and timestamp resolution on temporal reachability.
- Make results reproducible with the exact data snapshot and analysis parameters.
5.12. Event Time, System Time, and Derived Forensic Timelines
A single timestamp field rarely captures sufficient evidentiary context for a forensic timeline. File-system timestamps, application event time, server receipt time, database processing time, and the analyst's export time represent different occurrences. Collapsing them into one date can change apparent ordering or create a false impression of simultaneity. Preserve the source time zone, timestamp precision, possible clock offset, and serialization format.
Not all timestamps provide the same precision. If one source records seconds and another milliseconds, the apparent ordering must not be promoted into a definitive global order without justification. Overlapping uncertainty intervals mean that timestamp comparison alone cannot establish which event occurred first. Message sequence numbers, linkage identifiers, or independent observations may strengthen the conclusion when available; otherwise the uncertainty belongs in the report.
Every displayed event should retain the original record identity and the exact time field used for its position. Normalization, such as conversion to UTC, must preserve the original value alongside the derived one. Reproducing the same timeline from the same source records and transformation rules is a stronger forensic quality criterion than merely producing a visually persuasive chronology.
5.13. Usage and Transfer Artefacts of Removable Storage Media
Connecting removable media, opening a file, copying it, and transmitting it outside a system are distinct evidentiary propositions. Device identifiers, connection times, filesystem journals, paths, user-profile artefacts, and available application logs may be assessed together. Device reuse across ports and unreliable serial identifiers limit attribution.
A filesystem timestamp does not independently prove copying; timestamp semantics depend on the filesystem and acquisition tool. Validated data, inferential steps, and alternative explanations must remain separate in the examination copy. Evidence preservation requires distinguishing examination-generated access traces from source artefacts.
5.14. Logical Deletion and Physical Persistence in SSD and NVMe Media
On solid-state storage, the Flash Translation Layer maps logical block addresses to physical NAND cells. Wear leveling, over-provisioning, and bad-block management mean that rewriting one logical address need not overwrite its former physical location. TRIM or deallocate may mark logical content invalid without proving that all physical copies have been destroyed.
Forensic acquisition and media sanitization pursue opposite goals. Acquisition protects observable evidence and declares collection limitations; sanitization requires a supported device operation, suitable authority, completion status, and verification evidence. Cryptographic erase relies on effective destruction of the relevant encryption keys; its success cannot be assumed without establishing key scope and the presence or absence of backup keys.
Unit 6: Operating-System, Application, Identity, and Communications Artifacts
6.1. Windows
Typical Windows sources include Registry hives, Event Logs, Prefetch, LNK files, Jump Lists, browser databases, NTFS metadata, Volume Shadow Copies, and user-profile artifacts. An examiner should understand the mechanism that creates an artifact before attributing it to a human action.
6.2. Linux
Linux evidence may include journal data, syslog files, authentication records, shell histories, package databases, cron/systemd definitions, home directories, process state, and file-system metadata. In containerized environments, host, orchestrator, and container logs can have different retention and clock behavior.
6.3. macOS
APFS, Unified Logging, plist files, user Library data, Spotlight metadata, and cloud synchronization require assumptions different from legacy HFS+ analysis. Tool support must be matched to the relevant macOS and APFS versions.
6.4. Browsers, E-Mail, and Messaging
Browser history, cookies, cache, local storage, downloads, and profile databases can reconstruct user activity. Synchronized profiles require care because a record visible on one device may have originated elsewhere.
For e-mail and messaging, headers, server logs, message identifiers, delivery traces, and client-side copies should be correlated. A screenshot is weaker than the underlying structured record when the latter can be preserved.
6.5. Linking Examination Purpose to Method
Forensic examination is broader than criminal investigation. Technical examination can support:
- crime and misuse investigations,
- vulnerability and unauthorized-access analysis,
- reconstruction of user activity,
- relationship analysis across people/accounts/devices,
- dispute and incident resolution,
- incident response and root-cause analysis.
The purpose changes evidence priority. Shell history and application artifacts may dominate a user-activity investigation, while authentication logs, network telemetry, and connection records can be more important in an intrusion case.
6.6. Operating-System Logs
Logs are products of logging mechanisms; they are not direct copies of reality. An examiner should understand source configuration, retention, rotation, time source, and the possibility of missing records.
On Windows, channel, provider, Event ID, timestamp, and event payload should be interpreted together. On Linux, journald, syslog-family sources, authentication logs, kernel messages, and service-specific logs may provide different views. Application and web-server logs can use time and formatting conventions independent of the operating system.
6.7. Windows Registry and Configuration Artifacts
The Registry can describe user profiles, installed applications, services, recently used objects, autostart locations, device history, and system configuration. Registry hives such as NTUSER.DAT, SYSTEM, SOFTWARE, and SAM remain conceptually useful, although exact key locations and semantics can change across Windows versions.
A Registry entry is not automatically proof of direct user action. The operating system, installer, or application may create it. Registry findings should therefore be correlated with artifacts such as Prefetch, LNK files, Jump Lists, event logs, browser history, or file-system timestamps.
6.8. Installed Software and Execution Traces
Package records, installed-program lists, services, startup entries, and application directories describe system capability. “Installed” and “executed” are different claims. Evidence of execution may require process artifacts, Prefetch-like traces, application logs, shell history, or user-profile data.
6.9. Deleted Data and File Recovery
Deletion semantics vary among file systems. Some systems mark metadata entries as free; some return blocks to allocation structures; SSDs may propagate TRIM information to the storage layer. The common assumption that a deleted file is always recoverable is false.
Recovery can use two broad techniques:
- reconstruction from file-system metadata,
- file carving based on signatures or content structure.
Carving may not recover the original filename, path, or exact length, and fragmented files can be reassembled incorrectly.
6.10. Snapshots, Shadow Copies, and Prior Versions
Volume Shadow Copy and similar mechanisms can preserve earlier states of files. A snapshot is not the same thing as a backup. Its creation time, retention behavior, and the mapping between file versions and snapshots should be understood. Virtual-machine and file-system snapshots require the same kind of temporal reasoning.
6.11. Hex-Level Examination
A hex viewer exposes raw bytes without relying entirely on a high-level parser. It is valuable for validating file signatures, partition tables, slack space, damaged structures, and carving output. Hex is not self-explanatory: byte order, character encoding, and the relevant binary structure must still be known.
6.12. Metadata Analysis
File-system metadata, document metadata, media EXIF data, and application-database metadata belong to different layers. Even a phrase such as “creation time” can have different meanings at each layer. Copying, exporting, messaging, or cloud synchronization may rewrite timestamps.
6.13. Web History and Browser Artifacts
Browser examination extends beyond URL history. Downloads, cache, cookies, local/session storage, session state, form data, and extension data can answer different questions. Private-browsing modes do not guarantee that no trace exists elsewhere; DNS caches, network telemetry, and remote service logs may still be relevant.
6.14. E-Mail and Instant Messaging
The visible sender field is different from the transport path. RFC headers, Message-ID, Received lines, MIME structure, attachments, and server logs should be considered together. A local mail archive, webmail service, and mobile client may each retain different fragments of the same account history.
Messaging evidence can span message databases, media caches, notification artifacts, backups, and cloud synchronization. End-to-end encryption does not imply that decrypted data is absent from endpoint devices.
6.15. Indexing and Keyword Search
Indexing reduces search cost on large data sets, but the index is itself a transformation. Tokenization, character encoding, stop-word behavior, language, normalization, and unsupported file formats all affect results. “No hit” in an index is therefore not equivalent to “the data does not exist.”
A search set can contain words, e-mail addresses, domains, usernames, telephone numbers, IP addresses, hashes, regular expressions, and case-specific identifiers. Overly broad searches create noise; overly narrow searches can miss evidence.
6.16. Categorization and Filtering
Filtering by file type, known hash set, MIME type, size, time range, user, or directory can reduce the examination space. Known-good hash sets are useful for eliminating common files, but a hash identifies one exact byte sequence; a different build of the same application will have a different hash.
6.17. Booting or Virtualizing a Forensic Image
Booting a disk image in a virtual machine can help reproduce the user's environment, but a verified master image should not be mounted writeable. A derived working copy or copy-on-write layer should absorb changes.
Virtual hardware may not reproduce TPM, GPU, licensing, drivers, network, and clock behavior exactly. Booting is therefore complementary to artifact analysis rather than a replacement for it.
6.18. Intersection with Malware Analysis
A suspicious file's hash, signature, and path are only starting points. Static analysis examines structure, imports, strings, and code; dynamic analysis observes behavior in a controlled environment. Executing suspicious software on evidential systems is not a validation method.
Malware findings should be connected to process, network, persistence, file-creation, Registry, and credential-access artifacts and then placed on the incident timeline.
6.19. Digital Identity, Communications, and Location Artifacts
User activity is increasingly distributed across browsers, email, messaging clients, mobile apps, and remote services rather than confined to one computer's file system. These sources provide rich context but also carry a high risk of over-attribution.
6.20. Browser Artifacts
History, cache, cookies, downloads, form data, local storage, and session state answer different questions. A URL in browser history does not by itself prove an intentional visit by a particular person; redirects, prefetching, embedded resources, and synchronization can create records.
A safer reasoning chain is:
artifact -> this browser profile contains a record for the resource
correlation -> time + download + cache + session support one event
attribution -> additional identity evidence is needed for the physical actor
6.21. Email Headers and MIME Structure
The displayed From field is not sufficient source authentication. Transport headers, Message-ID, Received chains, timestamps, SPF/DKIM/DMARC results when available, server logs, and account-session evidence can be correlated. MIME structure determines how attachments and embedded objects are represented.
6.22. Messaging Applications and SQLite
Desktop and mobile applications frequently use SQLite or similar embedded databases. Active tables, WAL/journal files, and deleted pages may reflect different historical states. Schema versions can change across application updates, so a parser that assumes fixed columns may silently produce wrong results. Critical fields should be checked against raw data when necessary.
6.23. Location Data
GPS coordinates, Wi-Fi access-point observations, cellular identifiers, image EXIF, application location histories, and IP geolocation have different error models. None automatically proves that a person was physically present. Device possession, sensor source, synchronization, and shared accounts must be considered.
6.24. Social-Platform and Remote-Account Evidence
Social-media evidence should not be reduced to screenshots. When available, platform exports, account identifiers, content identifiers, timestamps, URLs, relationship records, and acquisition method should be preserved together. Screenshots are useful for visual context; structured data is more useful for search, timeline analysis, and correlation.
Unit 7: Live Response, Memory, and Malware Examination
7.1. Memory Acquisition
RAM can contain:
- processes and threads,
- active network connections,
- injected code,
- command history,
- decryption keys,
- session tokens,
- malware components absent from disk.
Memory acquisition itself modifies the machine. The acquisition tool’s footprint, driver requirements, platform compatibility, and generated artifacts should be documented.
7.2. Live versus Post-Mortem Examination
Live response gains volatile evidence but creates state changes. Post-mortem examination is more controlled but loses RAM, active sessions, and some decrypted content. The choice is risk-based, not ideological.
7.3. Malware Analysis
Hashes and antivirus signatures are only the start. Static analysis can inspect format, imports, strings, code structure, and embedded resources. Dynamic analysis observes process creation, file and registry changes, persistence, and network behavior in an isolated environment. Original evidence should not be executed directly when a verified working copy can be used.
7.4. Live Response, Memory, and Volatile Evidence
Examining a running system inevitably changes it. Executing a command creates processes, allocates memory, may write logs, and changes caches. The objective of live response is therefore not “zero change” but the smallest necessary, measurable, and justified change.
7.5. Deciding on Live Acquisition
Live acquisition can be especially valuable when:
- full-disk encryption is currently unlocked,
- memory may contain keys, sessions, or process state,
- fileless or memory-resident malware is suspected,
- active network connections and listening sockets matter,
- shutdown would cause greater evidential or operational loss.
Conversely, uncontrolled scripts or unvalidated tools can alter evidence unnecessarily. The decision should follow pre-established authority and procedure rather than improvisation at the scene.
7.6. The Evidential Surface of Memory
A memory image can contain:
- process and thread structures,
- loaded modules,
- open files and objects,
- network sockets,
- command or application buffers,
- authentication artifacts,
- some cryptographic keys,
- kernel objects and drivers,
- injected or concealed code.
A string found in memory should not automatically be attributed to a user. It may originate from an application cache, file cache, network packet, or another process. Structural context and correlation with disk or network artifacts are required.
7.7. Live-Response Ordering
A generic sequence can be expressed as:
time source
 -> users / sessions
 -> processes and services
 -> network connections
 -> open files / mounts
 -> memory acquisition
 -> critical configuration and logs
 -> persistent-media acquisition
This is not a universal fixed order. Volatility, platform, threat, and business-continuity constraints change priorities. What matters is that the selected sequence and its rationale are recorded.
7.8. Measuring Tool Impact
A live-response tool changes the host through its binary, libraries, drivers, and output operations. It should be:
- obtained from a trusted source,
- identified by hash,
- version-recorded,
- characterized on test systems,
- configured so output does not unnecessarily modify source media.
Output may be written to separate media or a trusted network target. Network transfer itself creates connections and traffic, so that effect belongs in the activity log.
7.9. Time, Drift, and Timezone
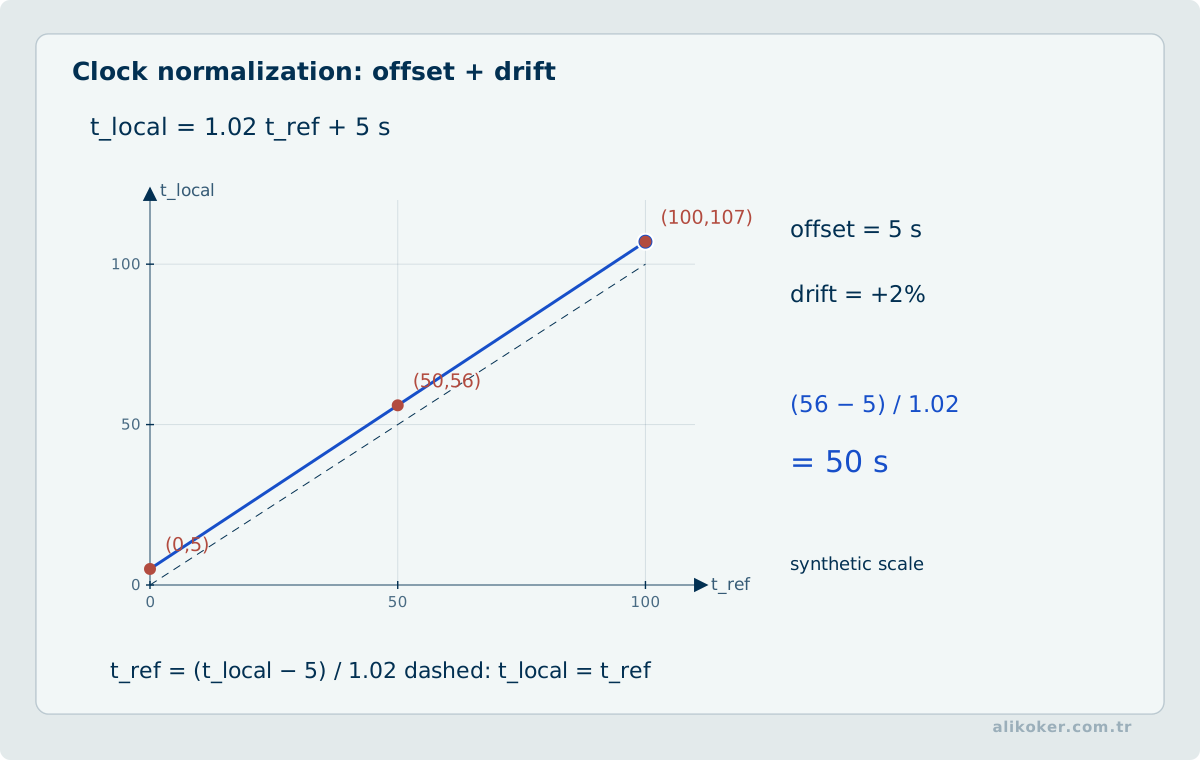
An incorrect device clock can distort an entire timeline. Local time, UTC offset, timezone configuration, NTP state, and observed drift should be recorded. Rather than “correcting” the source clock during acquisition, the discrepancy should be documented and normalized during analysis.
Unit 8: Network, Wireless, and Mobile Forensics
8.1. Packets, Flows, and Logs Are Different Evidence
A PCAP may preserve packet payload and protocol details. NetFlow/IPFIX-style flow records describe communication relationships and volumes with far less content. Firewall, DNS, proxy, VPN, and identity logs add product-specific semantic events.
packet -> protocol detail
flow   -> relationship and volume
log    -> product interpretation
These sources are complementary rather than interchangeable.
Wireshark is useful for protocol dissection and filtering, but correct interpretation requires protocol knowledge. Capture filters, display filters, TCP reassembly, NAT, proxies, tunnels, and encrypted traffic belong to different layers of analysis.
8.2. Encrypted Traffic
TLS does not eliminate network forensics. Payload may be hidden while endpoints, timing, volume, certificate metadata, DNS, and host-side logs still support correlation. TLS 1.3 and newer privacy mechanisms change which metadata is observable, so assumptions must be verified against the actual protocol and network architecture.
8.3. Mobile Device Forensics
Modern mobile devices combine strong encryption, secure boot, hardware-backed keys, application sandboxes, and cloud synchronization. The old model of “image all flash storage” is not universally available.
Acquisition can be viewed as a spectrum:
manual observation
  ↓
logical export
  ↓
file-system acquisition
  ↓
physical / low-level acquisition
Lower-level acquisition is not automatically more informative. Encrypted raw storage may expose less useful evidence than a semantically rich file-system acquisition performed while the device is legitimately unlocked.
First response should consider lock state, battery, network connectivity, remote-wipe risk, USB state, and active sessions. Radio isolation can be useful but may also change power consumption and device behavior.
NIST SP 800-101 Rev. 1 treats validation, preservation, acquisition, examination, analysis, and reporting as connected parts of mobile forensic practice.
8.4. Network Capture and the Wireshark Model
Tool-independent packet analysis has three stages:
- Capture: collect packets at the correct interface and observation point.
- Dissection: interpret Ethernet/IP/TCP/UDP and higher-layer protocols.
- Analysis: apply filters, stream reconstruction, statistics, and correlation to the case question.
Capture filters and display filters are not equivalent. A capture filter discards data before it is stored; a display filter changes only what is shown. Aggressive capture filtering can create irreversible evidence loss.
Typical questions include:
which DNS names did this endpoint query?
which TCP sessions show abnormal retransmission?
which host contacted unexpected external destinations?
which TLS sessions share a common SNI or certificate property?
8.5. Packets, Flows, and Sessions
A single packet is often insufficient context. Reassembling a TCP stream can reveal an application conversation. NetFlow/IPFIX-style records can show peers, ports, volume, and time without retaining full content. PCAP provides high detail at high storage cost; flow records trade detail for longer retention.
8.6. Wireless Artifacts
Wireless analysis can combine saved SSID/BSSID state, connection times, DHCP records, and access-point logs. A MAC address is not a definitive person identity; modern operating systems may randomize MAC addresses.
8.7. Mobile-Device Evidence Surface
Modern mobile forensics extends far beyond contacts and SMS. Evidence can exist in:
- application sandboxes,
- SQLite/Realm-style databases,
- keychain/keystore stores,
- notification data,
- media and thumbnail caches,
- location and sensor data,
- cloud backups,
- embedded web content,
- eSIM and network configuration.
Historical platforms such as Symbian, BlackBerry, Windows Mobile, MeeGo, and Bada remain useful for understanding the evolution of mobile forensics. Current examinations must select methods according to the present security model and device version.
8.8. Mobile Acquisition Levels
A rough hierarchy is:
manual observation
   ↓
logical backup/API
   ↓
file-system acquisition
   ↓
physical/bootloader-level acquisition
   ↓
hardware methods such as JTAG or chip-off
A lower layer is not automatically better. Hardware methods can be destructive, costly, or ineffective against modern encryption. The preferred method is the least invasive technique that can answer the examination question.
8.9. SIM and Subscriber Data
A SIM/UICC can expose subscription identifiers, network parameters, and limited user data. Most modern communication history is not stored on the SIM but on the device and within application/cloud stores. SIM data should be correlated with device artifacts, carrier records, and account information.
8.10. Mobile Media
Content analysis and metadata analysis are separate. EXIF timestamps and location can be rewritten or stripped. A thumbnail can remain after the original file has disappeared. Messaging applications may recompress images and remove metadata.
8.11. Signal Absence versus Data Absence in Wireless Evidence
Missing connection records do not automatically establish that a device emitted no radio signal or was absent from a particular area. Retention rules, missing logging, coverage, protocol differences, disabled interfaces, and tool capabilities affect the available observations. A Faraday enclosure also does not retroactively remove prior sessions or persistent metadata.
Three layers must be distinguished: physical RF observations, protocol or session records, and on-device application artifacts. Correlation requires explicit treatment of clock offsets, session identity, access points, and measurement coverage. Behavior or intent must not be inferred from a single record source.
This relates to electromagnetic-emission threats addressed in Cybersecurity Engineering, but the forensic issue is the evidentiary meaning of a negative result.
Unit 9: Cloud, Remote-Service, and Distributed-System Evidence
9.1. Cloud and Remote-Service Evidence
Cloud investigations often cannot center on a disk image. Relevant evidence can reside in:
- provider audit logs,
- object storage,
- SaaS exports,
- API responses,
- identity systems,
- snapshots and backups,
- management-plane activity.
Provider-derived evidence should record tenant/account identity, request time, API or export version, format, provider integrity metadata, time zone, and retention policy. SWGDE’s 2025 cloud-evidence guidance explicitly recognizes that provider-specific implementations make a single universal acquisition procedure impractical.
Multi-tenant infrastructure also means that seizing a physical disk may be impossible or inappropriate. Logical provenance and provider records therefore become central to the evidence chain.
9.2. Cloud Evidence as a Multi-Layer System
A “disk image” is often unavailable or incomplete in cloud environments. Evidence may instead consist of audit logs, object versions, IAM events, API calls, snapshots, serverless-function logs, container layers, or SaaS exports. Provider-side timestamps and account/tenant identity are essential context.
9.3. Time and Identity in Distributed Systems
Correlating logs across nodes requires explicit handling of clock drift, NTP synchronization, and time zones. Comparing displayed local times directly can create a false event order. Request IDs, trace IDs, session IDs, user/device identity, and network tuples can support correlation.
Unit 10: Search, Indexing, Correlation, and Large-Evidence-Set Analysis
10.1. Search Is an Engineering Operation
Keyword search depends on encoding, Unicode normalization, case rules, language, regular expressions, tokenization, compression, and index coverage. To reproduce a search, record:
query
search mode
encoding
case policy
regular expression, if any
scope
excluded data
tool and version
10.2. Correlation
Strong conclusions often emerge from independent artifacts rather than a single record. A claim that a file was copied to removable media, for example, may be supported by:
USB device history
+ file-system timestamps
+ LNK / Recent artifacts
+ user-session records
+ system event logs
The report should still distinguish observation from inference.
10.3. Relationship Analysis
Accounts, devices, IP addresses, phone numbers, file hashes, and timestamps can be modeled as a graph. Identity resolution requires caution: a shared IP, NAT address, common device, or reused number does not automatically represent one individual.
10.4. Timeline Engineering
A forensic timeline is not merely sorted file mtime values. Different artifacts represent different temporal semantics:
- event occurrence time,
- log-write time,
- synchronization time,
- copy/export time,
- parser-derived time.
Time zone and daylight-saving changes must be normalized without losing the original representation. A defensible timeline retains both source type and original time semantics for each event.
10.5. Correlation: from Artifact to Event Model
A strong inference often emerges when independent sources support the same hypothesis. A claim that a USB device was used, for example, can be supported by:
Registry device history
   +
setup/device logs
   +
LNK / Jump List artifacts
   +
file-system timestamps
   +
user-session timing
        ↓
stronger event model
Disagreement is equally valuable. It can indicate clock problems, deletion, another user, synchronization behavior, or parser error.
10.6. Relationship Analysis — Deeper Treatment
Graphs can connect people, devices, accounts, IP addresses, telephone numbers, files, and events. An edge should have a precise meaning. Sharing an IP address or Wi-Fi network does not by itself establish a direct human relationship.
account A --logged into--> device X
device X  --connected to--> IP Y
account A --messaged--> account B
A generic “related to” edge hides important evidential semantics.
10.7. Forensic Scalability
Terabyte-scale evidence sets and millions of files make exhaustive deep parsing expensive. A staged pipeline can preserve rigor while allocating expensive work effectively:
- evidence inventory,
- fast metadata extraction,
- known-file filtering,
- time/user scoping,
- indexing,
- targeted deep parsing,
- manual verification.
Filtering criteria should be retained so that the examination scope can be reproduced later.
10.8. Examination Workflow for Large Evidence Sets
Modern cases can involve hundreds of devices, cloud exports, mailboxes, packet captures, and mobile backups. The problem is not only data volume; it is reducing the search space without losing scope or provenance.
10.9. Known-File Sets and Hash-Based Reduction
Cryptographic hashes allow exact byte-identical files to be compared efficiently. Validated known-good operating-system or application files can be filtered, while known-malicious or otherwise significant hashes can be prioritized.
The limitation is clear: a one-bit modification changes a cryptographic hash completely. Similar-image, document, or transformed-media discovery may therefore use perceptual hashes or feature-based fingerprints. Such similarity functions must not be confused with cryptographic integrity verification.
10.10. Archives, Containers, and Nested Data
One file may contain many others: archives, mailbox containers, virtual disks, office documents, mobile backups, or databases. Recursive extraction needs explicit resource budgets because malformed or hostile inputs can consume excessive CPU, memory, or storage.
Every derived object should preserve its origin chain:
source image
 -> container
    -> archive
       -> embedded file
          -> parsed artifact
That chain lets a reportable finding be traced back to raw evidence.
10.11. Indexing, Encoding, and Search
Text search is not merely scanning ASCII or UTF-8. UTF-16, legacy encodings, compressed content, PDF/Office structures, and database fields require format-aware parsing. Keyword sets should:
- derive from case hypotheses,
- include context to control false positives,
- define case and language behavior,
- account for performance and traceability when using regular expressions.
A search-engine hit is not itself an evidential conclusion. Location within the source object, provenance, time, and identity context must still be examined.
10.12. Deduplication and Near-Duplicate Analysis
Exact duplicates can overwhelm a large examination. Cryptographic-hash deduplication is a strong first step. However, identical content with different metadata or provenance may still be evidentially distinct. A system should retain the relationship “one content object, N source occurrences” rather than discarding origin information.
10.13. Derived Evidence and Export
Thumbnails, converted images, extracted text, decompressed objects, database exports, and screenshots of virtualized systems are not the original evidence. They are derived artifacts. For important transformations it is useful to retain:
- source identity,
- tool and version,
- parameters,
- output hash,
- transformation time.
This supports independent verification and later reprocessing.
10.14. Reconstruction of Digital Document Provenance and Transfer Chains
Document provenance analysis tests relationships between source objects and derived files. Content hashes, file formats, application metadata, version history, access logs, and storage artefacts identify the same document at different evidential levels. An identical byte-level hash strongly supports content equality; a different hash does not necessarily establish semantic difference.
Each edge in a source → access → possible copy → export reconstruction requires an evidence reference and an uncertainty assessment. Finding a file on storage media does not prove its transmission to a third party. Clock offsets, application-modified timestamps, and missing events may yield only a partial order; uncertain links must not be represented as direct observations in an event graph.
10.14.1. Validation of File Reconstruction from Network Streams
A file transferred over a network cannot always be obtained by simply concatenating captured packets. After transport-layer byte-stream reconstruction, the application layer must resolve message boundaries, transfer encodings, compression, file offsets, and completion conditions. In HTTP chunked transfers, chunk-length markers are not part of the application body; partial-content responses place data according to their declared byte ranges.
A derived artifact should record source_capture, flow_id, packet_ranges, content_transform, covered_byte_ranges, and completion_status. The digest of original captured bytes and the digest of the reconstructed, possibly transformed file identify different objects. Decompression, header removal, and content transformation must be reproducible in their actual execution order.
Classifying the output as complete, partial, inconsistent, or unsupported prevents a partial file from being presented as complete. File signatures, declared sizes, and captured byte-range coverage must be validated independently; consistency of one property does not establish completeness.
10.14.2. Range Merging and Overlap Management in Fragmented Files
Coverage of offset-addressed file fragments can be modeled as the union U = ⋃[a_i,b_i) of half-open byte intervals. Given a declared total file length L, completeness can be assessed only when |U| = L and every offset has consistent content. The sum of received fragment sizes equaling L is insufficient because fragments may be duplicated.
Sorting intervals by starting offset and merging adjacent or overlapping intervals takes O(n log n) sorting time and O(n) merge time in the general case. Different bytes received for the same range must be reported as inconsistency; silently selecting the first or last version introduces an unreported forensic assumption. Gaps filled with zeros cannot be labeled original evidence.
Source packets, declared file identity, fragment offsets, and confidence of reconstruction must remain distinct attributes. Length overflow, negative offsets, conflicting overlaps, and large sparse files belong in the required boundary-condition test dataset.
Unit 11: Tool Ecosystem, Validation, Repeatability, and Quality Assurance
11.1. Tool Output Is an Interpretation
A clean table produced by a forensic suite is an interpretation of underlying bytes. Unsupported versions, parser defects, changed schemas, or misunderstood timestamp semantics can produce convincing but incorrect results.
Critical findings benefit from layered verification:
raw source
  ↓
tool A parsing
  ↓
independent tool / manual verification
  ↓
semantic consistency check
Media or messaging evidence may pass through several transformations: the original recording, transcription, time-aligned utterance, search result, and analytical summary. Errors in an early transformation can affect downstream claims. Preserving the distinction between source records and derived artifacts makes it possible to reconstruct how a particular conclusion was produced.
The NIST Computer Forensics Tool Testing program publishes testing methods and reports for forensic functions. The NIST Tool Catalog is useful for discovering tools and capabilities, but catalog inclusion does not mean that NIST has independently validated a particular product.
11.1.1. Differential and Reproducible Validation of Network Parsers
A forensic network parser is a measurement instrument that converts raw captures into protocol fields and derived artifacts. Validation can combine synthetic PCAP fixtures with known expected results and comparisons against independent implementations. Agreement between two tools is not conclusive because both tools can share an incorrect assumption.
Test cases should cover missing initial packets, reordering, duplicate bytes, malformed length fields, ambiguous protocols, timestamp resolution, and incomplete reconstructed files. Each test records the source byte range, expected state, observed state, and rationale for discrepancies. The same input, tool version, and normalization parameters should yield the same substantive findings.
Equivalent captures presented in different packet orders should be tested separately when order independence is a claimed property. Variations in timestamps, wall-clock ordering, unstable map iteration, or concurrent completion order can produce nondeterministic reports.
11.2. Repeatability and Reproducibility
- Repeatability: obtaining comparable results with the same method and conditions.
- Reproducibility: enabling an independent examiner or environment to verify the result.
ISO/IEC 27042 emphasizes continuity, validity, repeatability, reproducibility, and sufficient documentation for independent scrutiny.
A reproducible text finding needs a stable source identifier, parser or transcription version, language and normalization policy, source offsets, and query conditions. Two tools may legitimately produce different parses; the difference should be documented rather than silently resolved. A SHA-256 digest compared with a trusted acquisition reference supports byte-level integrity after collection, but it does not by itself authenticate the original source or prove the correctness of its timestamps.
11.3. Methodological Validation of Anti-Forensic Indicators
When a tool reports deletion, timestamp changes, or inconsistent logs, first validate the detection method. Unit 13 examines the technical interpretation of such indicators, normal causes, and limits of examination.
11.4. Tool Ecosystem and Historical Products
Write blockers from vendors such as Tableau and WiebeTech, forensic suites such as FTK, EnCase, X-Ways, OSForensics, Nuix, Belkasoft, Autopsy/Sleuth Kit, and mobile tools such as XRY, UFED, and Oxygen are historically and operationally useful examples, but a product name is not a proof of correctness.
A forensic tool should instead be evaluated by capability:
- acquisition and verification,
- file-system parsing,
- deleted-data recovery and carving,
- indexing and search,
- Registry/OS artifact parsing,
- e-mail and messaging analysis,
- mobile extraction and parsing,
- network analysis,
- memory analysis,
- reporting and export.
Parser behavior can change between versions. Critical findings should be verified with a second tool, raw data, or an independent method when feasible.
11.5. Validation Before Operational Use
A forensic laboratory should maintain known-answer test sets. A test image can contain known files, deleted objects, timestamps, multiple file systems, and malformed structures. Expected results are documented in advance and regression tests are run after tool updates.
Known-answer sets should also contain deceptive negatives: distinct people with identical names, timezone shifts, truncated files, malformed encodings, and duplicated communication records. A search or graph interface that produces plausible results may still omit records because of pagination, access scope, or retention boundaries. Completeness must therefore be part of the validation protocol.
known input
   ↓
tool + version + configuration
   ↓
compare with expected output
   ↓
document limitations if results diverge
11.6. Generalizing the FTK/Forensic-Suite Workflow
FTK-style tabs and imaging procedures can be generalized into the common workflow of a forensic suite. A typical suite:
- adds evidence sources to a case,
- parses file systems,
- classifies files by type and metadata,
- builds a search index,
- searches keywords and structured values,
- presents specialized views for e-mail and media,
- bookmarks relevant items,
- exports selected objects and reports.
Convenience should not hide the underlying data model. If a suite marks a file as “Deleted,” the examiner should understand which file-system structure supports that interpretation before reporting it.
Relationship diagrams raise a similar semantic issue. A recorded communication between two parties and the appearance of their names in separate texts are different kinds of connections. An edge derived from textual similarity should not be presented as a verified communication without retaining its source and matching rule. Aggregating repeated communications for analysis must not erase the underlying record multiplicity.
11.7. Laboratory Quality System
Quality assurance begins long before the final report. A mature forensic laboratory maintains:
- hardware and software inventories,
- version control,
- known-answer test images,
- validated standard operating procedures,
- time-source checks,
- hash and chain-of-custody controls,
- peer review,
- deviation/error records,
- regression testing after tool updates.
This turns individual expertise into a repeatable organizational capability.
11.8. Causal Limits of Image Compression Traces
JPEG blocking patterns, quantization traces, and indications of double compression can offer clues about an image's processing history, but none proves intentional manipulation by itself. Resaving, messaging-app transcoding, resizing, and different encoder chains can produce similar patterns. The observed statistical trace must be distinguished from its proposed cause.
Discontinuities near an 8×8 DCT block grid can be examined. A region with a different compression trace may support a local-editing hypothesis, yet resampling and local image content can also affect that trace. Evidence of double JPEG quantization depends on the earlier quality setting and block alignment; some recompression sequences leave little diagnostic signal. A negative result does not establish that no manipulation occurred.
Forensic reporting separates the source file from derived working copies and preserves the hashes and parameters of each transformation. A conclusive assertion should not rely solely on one filtered image. False-positive behavior should be tested across cameras, image content, quality settings, and resizing conditions. Findings should, where possible, be evaluated alongside metadata, source-file provenance, and independent examination methods.
11.9. Validation of Multimedia Examination Methods
Audio and image examination methods should be evaluated on reference material with known properties. Assess false-positive and false-negative behaviour under changes in capture conditions, codecs, resampling and enhancement.
Improved intelligibility of an enhanced file does not validate details absent from the source. Check comparability of reference and questioned samples in resolution, channel response and processing history.
11.10. Methodological Validity and Approaches across Legal Systems
The Daubert standard and ACPO principles are useful in their respective legal and methodological contexts. They belong to particular legal contexts and should not be treated as universal legal rules. Their enduring technical lessons are methodological: minimize unnecessary changes to original data, document necessary changes, use competent personnel, make methods explainable, and preserve enough provenance for independent review.
Daubert and ACPO approaches do not replace expert-witness law in Türkiye. The key forensic controls are method suitability, disclosure of errors, protection of original data, and auditability of examination steps.
Unit 12: Encryption, Passwords, and Evidence Accessibility
12.1. Encryption, Passwords, and Accessibility
Integrity and accessibility are different problems. An encrypted image can be acquired and hashed correctly while its contents remain unavailable.
Authorized recovery strategies may include:
- logical acquisition from an already-unlocked session,
- volatile key material,
- enterprise key management,
- backups or synchronized replicas,
- password-recovery workflows,
- service-provider exports.
Password-search feasibility depends on the KDF, work factor, password distribution, and available hardware. “A GPU can crack any password” is not a technically defensible claim.
12.2. Password and Encryption Limits
When encrypted content is found, the encryption layer should first be identified: full disk, partition, file, archive, application database, or communication protocol. Password-recovery activity must remain within legal and resource constraints. GPU-assisted guessing rates depend heavily on the password scheme; generic claims that encryption is “breakable” or “unbreakable” are not technically useful.
A mounted encrypted volume on a live system can make volatile evidence especially important because keys or decrypted content may disappear at shutdown.
Unit 13: Anti-Forensics and the Limits of Examination
Why a digital record is missing can be as important as finding one. A record may never have been created, may have expired under a retention policy, may have been removed automatically, overwritten, made inaccessible, or deliberately altered. These possibilities do not support the same technical conclusion. Examination must verify the observed condition without inferring causation that the data cannot support.
13.1. Anti-Forensics and Its Effects on Examination
Anti-forensics is an umbrella term for actions that make digital traces harder to acquire, preserve, analyze, or interpret accurately. Deletion, record modification, concealment, misleading content generation, and disruption of event traces can be examined in this context. The same indicators can arise from normal system behavior. Evidence of a cleanup operation alone identifies neither an intent to conceal evidence nor an actor.
First establish the expected recording mechanism: which component records the event, under which conditions, whether logging is enabled, how long records are retained, who can access them, and whether they are forwarded elsewhere. Then compare that model with the observed state. A technical concern rests on a verified difference between an explainable recording expectation and actual observations, not merely on an unusual file.
Detailed instructions for conducting anti-forensic actions are outside this course. The focus is on detection indicators, alternative explanations, and examination reliability. University research on forensic examination provides a technical reference for the subject.
13.2. Absence of Data and Absence of Evidence
Failure to find a record does not prove that the record never existed or that the relevant event did not occur. Four boundaries determine the meaning of a negative finding:
- Scope: Which devices, accounts, locations, and time periods were examined?
- Generation: Would the system normally generate a record if the event occurred?
- Retention: What retention, deletion, and rotation policies applied?
- Access: Were any regions unavailable because of permissions, encryption, defective sectors, or incomplete exports?
For example, a missing entry within a particular period becomes meaningful negative evidence only after verifying that the log is complete, was enabled for that event, and covers the period in question. Systems outside the examination scope and unknown retention conditions must be stated in the conclusion.
An appropriate statement is: “No entry of the requested type was found for the specified interval in the records supplied.” A stronger claim requires separate evidence of the recording mechanism's reliability.
13.3. Deleted and Modified Data
Logical deletion may remove a file's visible directory entry while its physical bytes remain temporarily available. Overwriting, loss of encryption keys, file-system cleanup, and SSD TRIM or garbage collection affect recoverability in different ways. The disappearance of a file path is not identical to physical erasure of its contents.
Examination considers the storage technology, file-system format, active features, device use before acquisition, and acquisition method. If only part of a deleted file is recovered, limitations in content integrity and context must be recorded. File carving based on signatures does not necessarily restore the former path or establish a user association.
Before inferring intentional deletion, consider routine lifecycle operations, automated maintenance, retention policy, and application behavior. Unit 5 explains file-system and recovery techniques; this unit addresses the evidential limits of deletion indicators.
13.4. Timestamp and Metadata Manipulation
File timestamps have different meanings at the file-system, application, operating-system, and export layers. Creation time, modification time, last-access time, and journal timestamps do not necessarily refer to the same event. When timestomping is suspected, compare internal consistency first and independent time sources second.
Consider time zones and daylight-saving conversions, clock synchronization, resolution, file-copy and restore effects, virtual-machine snapshots, and application-generated metadata. An old timestamp alone is not proof of manipulation. Where timestamps conflict, distinguish original values from converted timestamps and values derived during examination.
A technical conclusion should test at least two plausible explanations for a timing discrepancy. When the underlying source record is unavailable, “the timestamp could not be consistently verified against available records” is more defensible than “the timestamp was altered.”
13.5. Deleted or Modified Logs
Event logs are not necessarily continuous or complete. Circular size limits, log rotation, interrupted central forwarding, unsynchronized clocks, dropped packets, and permission failures can create apparent gaps. Before assessing possible log deletion or alteration, validate the normal logging architecture.
Potential corroborating sources include local logs, a central log repository, security devices, identity providers, and application audit trails. Their independence matters: two dashboards derived from the same log are not two independent sources. Event identifiers, sequence fields, signatures, file modification information, and known forwarding delays must be considered together.
An examiner identifies technical indicators of possible log manipulation but does not attribute a missing record directly to an individual's intervention. Any unknown coverage of the logs must be disclosed.
13.6. Concealment, Encryption, and Obfuscation
Extension/content mismatches, embedded archives, multilayer containers, steganography, packing, and code obfuscation may complicate analysis. Encryption, compression, and access controls also serve legitimate security purposes. Their presence alone does not establish a concealment motive.
Examination distinguishes actual file format, embedded content, dependencies, application context, key management, and inaccessible portions. High entropy may indicate compression or encryption but does not, by itself, prove hidden content or deliberate concealment. If content is transformed or decrypted, record the key used where appropriate, tool, version, and resulting output as separate derived evidence.
Unit 12 covers the technical and authorization limits of accessing encrypted material. This section evaluates only the evidential strength of concealment indicators.
13.7. Fabricated and Misleading Digital Artifacts
A record, file, or media item can be technically well formed without having originated in the claimed event. Edited metadata, transplanted session records, re-encoded media, and synthetically generated content require provenance analysis.
Compare file structure, creation and transfer history, independent device or server records where available, signatures, original sources, and processing history. Visual or acoustic coherence does not prove authenticity. Error rates of detection tools for generative-AI content must also be considered. Unit 15 explains how derived evidence is linked to its original source.
If provenance cannot be verified, distinguish “the item is present in the examined material” from “the item was created by the claimed source during the claimed event.” The latter needs additional technical support.
13.8. Alternative Explanations and False Positives
Every apparent anti-forensic anomaly should be compared with ordinary operations. Automated cleanup, updates, restoration, synchronization, user error, disk faults, and logging configuration can produce similar effects. A tool alert is not itself a verified forensic finding.
A disciplined sequence is: define the observation; verify its source; establish normal behavior; test plausible alternatives where possible; disclose missing records; and state only supported technical conclusions. Known false-positive and false-negative rates should be discussed in their proper context. Unknown rates must not be replaced with invented numerical confidence.
An anomaly score is neither an intent score nor a measure of guilt. Statistical methods are covered in Anomaly Detection.
13.9. Limits of Technical Findings
An incomplete forensic image, unreadable sectors, unavailable keys, missing central logs, unknown clock offsets, or invalid parsing limits the scope of a technical conclusion. The report should distinguish the type of limitation, affected evidence, questions affected, and whether the limitation can be resolved.
Failure of a method does not mean absence of evidence or non-occurrence of an event. The evidential weight of a negative result depends on the conditions under which the method could detect the relevant state. If examination cannot be completed, notify the appointing authority of the reasons and any authorized alternative methods.
The operative distinction is clear: missing data, altered data, technical uncertainty, and allegations of intent are separate analytical layers. Confusing them can produce an unsound conclusion even when the examination tools are sound.
Unit 14: Scalable, Deterministic, and Auditable Forensic Architecture
14.1. Scalable and Auditable Forensic Architecture
At scale, digital forensics becomes a pipeline across acquisition, parsing, indexing, correlation, analyst review, and reporting rather than a purely manual desktop workflow. Performance matters, but determinism and auditability matter more.
14.2. Separating Stages in the Pipeline
Raw evidence and derived information should remain distinct:
immutable raw evidence
   -> verified working copy
      -> parser/decoder output
         -> index and features
            -> correlation
               -> analyst finding
                  -> report
Raw evidence remains unchanged. Reprocessing with a newer parser version can produce a separate derived dataset so that tool-version effects are measurable.
14.3. Parallelism and Deterministic Results
Independent objects can often be parsed in parallel, but concurrency should not make semantics or error handling nondeterministic. Job identity, source hash, parser version, configuration, and deterministic normalization help ensure that the same input under the same version produces the same evidential meaning.
14.4. Fault Isolation
One malformed object should not stop an entire case. Parser failures should be:
- bound to the source object,
- classified and recorded,
- isolated from unrelated processing,
- eligible for retry or independent verification when significant.
A silently skipped object is more dangerous than an explicit failure because analysts may assume the corpus is complete.
14.5. Audit Trail and Access Control
In a multi-user laboratory, it should be possible to determine who opened evidence, performed exports, changed findings, and released reports. Operational audit logs do not replace chain of custody, but they strengthen it.
Case-scoped authorization, least privilege, sensitive-content classification, and export policy keep the forensic platform itself from becoming a new disclosure channel.
14.6. Performance versus Correctness
Pre-indexing, hash filtering, parallel parsing, and incremental timeline construction can provide substantial performance gains. Optimization must not discard provenance or validation. A useful priority order is:
correctness and integrity
 -> traceability
    -> repeatability
       -> coverage
          -> performance
Unit 15: Provenance and Evidence References for Derived Analytical Findings
Raw digital evidence and an analytical result derived from that evidence are not the same object. Search indexes, timelines, relationship graphs, clustered events, and automated classifications are derivatives that can accelerate examination but do not replace the original evidence.
A defensible chain keeps the stages explicit:
original data
  ↓
verified working copy
  ↓
parsed record
  ↓
normalized event
  ↓
derived feature
  ↓
analytical finding
  ↓
reported interpretation
Each stage should retain a path back to the stage that justified it.
15.1. Canonical Record Identity
The same event can appear in multiple exports, reprocessing passes, or analytical views. A stable canonical identity helps prevent one observation from being counted as several pieces of evidence.
The deduplication rule must be explicit:
same canonical identity
 -> same event family

newer processing version
 -> may supersede an older derivative

different source identity
 -> must not be silently merged
Idempotence is a useful verification property:
D(D(X)) = D(X)Running the same deduplication procedure twice should not remove additional valid observations.
15.2. Immutable Analytical Snapshots
If the record set changes silently during examination, the same analytical question may produce a different result without a defensible explanation.
A versioned snapshot can bind one analytical state to:
snapshot v12
├─ source record set
├─ filters
├─ observation period
├─ parser version
├─ normalization version
└─ derived indexes
New evidence produces a new snapshot rather than mutating the previous one. A report can then be reproduced against the exact analytical state that created it.
15.3. Derivation Chains in Audio and Text Analysis
Audio-oriented examination can place several transformation layers between source media and a textual or statistical finding. A typical chain is:
source media
  ↓
codec decoding / canonical sample representation
  ↓
voice-activity or speech segmentation
  ↓
transcription
  ↓
normalized text for retrieval
  ↓
analytical feature or finding
Each stage is derived from the previous one. A transcript is not the source audio itself, and a normalized token stream is not a verbatim representation of the transcript. Case folding, morphological normalization, or character-level variants may be appropriate for indexing, while evidence shown to an examiner should point back to the original passage and, where possible, the original media interval.
The two representations therefore serve different purposes:
- normalized representation: matching, indexing, and analytical computation,
- original representation: review, evidence display, and independent verification.
Repeatability is stronger when a finding retains source identity, its location within the media or document, the transformation applied, and, where material, the tool or version that produced the derivative.
Errors introduced by silence segmentation, speaker separation, or transcription can propagate into later relationship and frequency analysis. A more sophisticated downstream model does not automatically repair an error that entered earlier in the derivation chain.
A transcript derived from a recording is an interpreted representation rather than the original audio evidence. Word recognition error, speaker attribution error and punctuation inference have different forensic consequences. Each derived finding should retain the source recording, time span, model or method version and the scope of any human verification. Thematic coding or automated classification adds a further derivation layer. A model-generated label should not be presented as evidence detached from the underlying audio or text span. Anonymizing individual examples also does not necessarily remove re-identification risk when records can be linked across datasets.
15.4. Findings Should Carry Evidence References
A derived finding should contain more than explanatory prose. Where possible, it should identify the observations from which it was computed:
finding
├─ finding type
├─ computed value
├─ method / version
├─ analytical scope
└─ evidenceRefs[]
This directly supports the question: “Which source observations contributed to this result?”
The same connection benefits interactive examination. An analyst should be able to move from a graph edge, temporal candidate, or relationship summary back to the underlying records.
15.5. Preservation of Canonical Evidence Identifiers
A forensic analytical system should not manufacture a critical record identity from similarity or fuzzy matching. A value should be bound to a sensitive action only when it comes from a trusted source such as an explicit source record, direct user input, or a previously verified result reference.
Choosing the closest-looking identifier can create a serious evidence-navigation error.
15.6. Transformation Manifest
Reproducibility requires more than an application name. A transformation manifest can include:
source hash
parser / tool version
normalization version
algorithm version
parameters
filters
snapshot version
output hash
This manifest does not need to disclose every internal implementation detail. It needs to preserve the technical contract required to reproduce the result.
15.6.1. Source and Transformation Traceability for Network-Derived Artifacts
A file, session, identifier, or audio recording derived from network evidence is an analytical object distinct from the original capture. Every derivative should be reproducible from the source-capture identity, packet ranges, direction, parser version, options, and transformation sequence. Each edge of a source -> parsed_message -> reconstructed_stream -> artifact chain records the transformation type and validation status.
The capture digest establishes integrity of the original capture file; the derived-file digest identifies the reconstructed byte sequence. Possession of both digests does not automatically prove the lineage between them. Stream offsets, source-frame identifiers, and a transformation manifest are required to preserve that relationship.
Missing packets, discarded malformed headers, decompression failures, and silence samples synthesized during codec processing must be visible in the manifest. Observations, algorithmically derived results, and analyst interpretations must be distinguishable in reports.
15.7. Separate Source Observation, Feature, and Interpretation
A defensible report distinguishes source observation, derived feature, and expert interpretation.
source observation:
  value actually present in the data

derived feature:
  measure computed from source observations

expert interpretation:
  meaning of that measure in the context of the event
Graph centrality is a derived feature, not proof of real-world importance. A temporal anomaly is an analytical candidate, not proof of legal or behavioral significance.
15.8. Evidential Limits for Synthetic and Altered Media
Analysis of audio or images must distinguish the original source, subsequent processing, encoding traces, and derived analytical findings. Compression, resampling, denoising, and transmission chains can produce artifacts resembling intentional alterations. Absence of a detectable artifact does not prove authenticity, while a suspicious feature alone does not prove deliberate manipulation.
An analytical record should preserve a content digest of the source, the order of transformations, resolution or sample-rate parameters, analysis window, and decision threshold. Performance established on one evaluation distribution must not be assumed for out-of-distribution material. Findings should connect observed feature → method → uncertainty → alternative explanations; definitive claims about an entity or event require independent corroboration.
15.9. Provenance in Interactive Analysis
Modern examination is often non-linear. A user can move from a graph node to a timeline, then to source data, then to a different correlation.
Provenance must survive this navigation:
selected finding
 -> derived records
 -> source record identifiers
 -> original file / acquisition source
A new filter creates a new analytical view; it should not rewrite the evidence basis of an earlier finding.
15.10. Auditability and Boundaries of Internal Model Reasoning
Auditability does not require exposing every private implementation detail or internal reasoning trace. It requires verifiable technical artifacts such as:
input
method
parameters
scope
output
evidence reference
version
Derived analytics become a reliable forensic component only when their relationship to source evidence, transformation method, and analytical scope remains explicit.
15.11. Hypothesis-Based Inference from Incomplete and Indirect Evidence
Direct observations, tool-derived features, statistical results, and expert interpretations are separate data types in a forensic model. An observation E may be evaluated against competing explanations H₁ and H₂; compatibility with E does not establish the truth of a proposition. Absence of an artefact is not evidence of absence unless the system's logging behavior and the completeness of acquisition have been established.
Evidential weights from multiple sources cannot be added while ignoring conditional dependence. Two logs derived from a single event are not independent corroboration. Every conclusion must identify examined sources, the covered time interval, validation methods, and plausible alternative explanations.
15.12. Engineering Checklist
1. verify authority and scope
2. inventory potential sources
3. rank volatility and loss risk
4. preserve source state
5. justify the acquisition method
6. verify integrity
7. separate source evidence from working copies
8. record tool and version
9. independently verify critical findings
10. validate clock and time-zone semantics
11. separate observations from interpretations
12. state limitations
13. make the report reproducible
Digital forensics engineering is therefore less about memorizing a large collection of tools than about controlling the transformation chain from source evidence to defensible conclusion. Tools, file systems, mobile platforms, and cloud services will change. Authority, integrity, traceability, validation, reproducibility, and disciplined interpretation remain the durable principles.
15.13. Provenance between Source and Derived Multimedia Evidence
Spectrograms, denoised audio, transcripts, cropped frames and comparison images are distinct outputs derived from audio or visual evidence. For each output, retain its source interval, processing parameters and operation order. Provenance should support navigation from a reported finding to a working derivative and then to the source.
Reports distinguish objective measurements from expert interpretation and identify uncertainty, alternative mechanisms and non-comparable recording conditions.
15.14. Traceability of Source Evidence, Derived Data, and Model Output
A spectrogram, transcript, face embedding, or relationship graph produced from digital evidence is a derived artifact, not the source itself. Each derivative is linked to the source evidence identifier, original time or sample range, processing version, parameters, and resulting artifact. Model-generated labels, transcripts, or similarity scores are not automatically promoted to directly observed facts; uncertainty and alternative explanations remain part of the analysis.
Reproducibility requires both consistent results under fixed inputs and software versions, and traceability of differences after a model or parameter change. A chain-of-custody record does not itself establish algorithmic correctness; evidence integrity, method validity, and the limits of expert interpretation are separate assurance layers.
15.15. Components of Evidence Confidence
A useful mental model is:
source reliability
× acquisition integrity
× parser correctness
× contextual correlation
× disciplined interpretation
This is not a numerical probability formula. It is a reminder that a weak link should reduce the strength of the stated conclusion.
The phrase high confidence must specify what has been measured. A matching hash concerns integrity; confidence in entity resolution concerns identity matching. An algorithm's score or agreement between examiners is not automatically a probability that an evidential claim is true.
15.16. Evidential Weight of Anomalies and Red Flags
An inconsistent timestamp, unusual access time or elevated event frequency can justify investigation but does not establish intent or actor identity. Clock reliability, logging delay, missing records and authorised workflows are competing explanations. Raw evidence, anomaly scores, analyst judgments and independently verified findings should be kept distinct. Statistical red-flag methods are discussed in Anomaly Detection.
Unit 16: Capture, Identity, and Time Correlation in Network Evidence
One of the most dangerous reasoning errors in network forensics is treating an address observed in a packet as a direct identity for a real person or device. Network evidence gains meaning only when capture location, address translation, time, service records, and application identity are correlated.
16.1. Capture Location Changes the Meaning of Evidence
The same session can look different at different points in the network:
client
  ↓
NAT / CGNAT
  ↓
organization boundary
  ↓
proxy / load balancer
  ↓
application
A private client address, a public egress address, and the proxy address recorded by the application can all represent the same communication path. The location of a PCAP or flow sensor therefore determines the address namespace visible in the evidence.
At minimum, capture provenance should record:
- sensor/interface identity,
- capture start and end time,
- clock source and time zone,
- snap length and capture filter,
- drop counters or capture-loss information,
- link-layer type,
- file integrity value,
- tool/version and relevant configuration.
A readable capture file is not proof of complete capture. Kernel rings, NICs, SPAN/TAP paths, and storage can drop traffic. If capture loss is unknown during a high-rate event, "the packet was not observed" is not equivalent to "the packet did not traverse the network."
16.2. PCAP/PCAPNG and Derived Outputs
A raw packet capture, a parsed CSV/JSON export, and a filtered screen view are different evidence layers:
raw capture
  ↓ validated parser
protocol fields
  ↓ filter / correlation
finding
A tool-generated "TCP stream," "expert info," or "malicious" label is a derived interpretation, not the source evidence itself.
Formats such as PCAPNG can carry multiple interfaces and additional capture metadata, but the presence and correctness of those fields must be verified for each file. A capability of the format is not proof that a particular capture contains trustworthy metadata.
A packet absent from a capture has not thereby been proven absent from the network. Capture position, filters, NIC offload, buffer overflow, clock settings, and capture start time limit observability. A gap in TCP sequence numbers may reflect network loss or packets missed locally, and one capture may not distinguish the causes. Forensic reporting should record capture position, filter, dropped-packet counters, and timestamp resolution. Reconstructed stream text is a derivative artifact and must not replace the original packet evidence.
16.2.1. PCAP Timestamp Resolution and Normalization Errors
The classic PCAP global-header format distinguishes whether timestamp fractions represent microseconds or nanoseconds. The fractional field must be scaled correctly together with the per-record seconds field. Applying a fixed 10⁻⁶ second scale to a nanosecond-resolution capture distorts the timeline and intervals between closely spaced packets.
Validation can encode the same packet sequence at different timestamp resolutions and compare normalized absolute times and interpacket intervals against expected values. PCAPNG additionally requires attention to interface-specific time-resolution and time-offset options. A format that is unsupported is a different condition from a format that is parsed incorrectly.
Monotonic time, UTC wall-clock time, and capture-device clock drift must remain separate concepts. The accuracy of timestamps used for ordering should be reported; equal or overlapping timestamps do not establish physical event causality without additional evidence.
16.3. NAT, CGNAT, DHCP, and Port-Time Correlation
A public IP address is not necessarily an endpoint identity, particularly behind NAT or carrier-grade NAT. Attribution may require port and time correlation:
public IP + source port + timestamp
        ↓
NAT / CGNAT mapping log
        ↓
private IP / subscriber context
        ↓
DHCP lease / access log
        ↓
endpoint / account evidence
Clock resolution and clock skew directly affect this chain. If one system records seconds while another records milliseconds, or if NTP offsets differ, several nearby sessions can be matched incorrectly.
Reports should therefore avoid language such as "the IP belongs to the person" when the evidence only proves an address assignment. Subscriber allocation, device use, account use, and a human action are different evidentiary layers.
16.4. TCP Reassembly and Packet-Capture Visibility
A TCP byte stream is independent of packet boundaries. One application message can span several segments, and one segment can contain multiple application messages. Retransmission, out-of-order arrival, and capture loss influence reassembly.
Consequences include:
- searching payload in isolated packets can miss an application transaction,
- counting retransmitted bytes twice can distort volume analysis,
- checksum offload can create apparent bad checksums in host captures,
- GRO/LRO/TSO can make host-side capture different from the physical wire representation.
Packet analysis should therefore account for the capture layer rather than assuming that a packet analyzer screen is a literal copy of every frame on the wire.
16.4.1. Direction, Completeness, and Inference Limits in Partial TCP Sessions
A capture may begin after the TCP three-way handshake. Client and server roles may then be inferred from ports or the first visible application message; such inference is not equivalent to direction confirmed by SYN/SYN-ACK observations. Separate sequence spaces, data gaps, and capture-time boundaries must be maintained for both directions.
Session properties can be represented by independent flags such as handshake_observed, direction_inferred, sequence_origin_unknown, gap_detected, and termination_observed. If the initial sequence number is missing, offsets may be relative to the first captured byte without claiming that it is the beginning of the actual stream. A missing FIN or RST may indicate an incomplete capture rather than a connection that remained open.
A forensic report must distinguish observed bytes, reassembled intervals, heuristic role assignments, and missing ranges. Even if an application protocol is identified, unavailable payload cannot support claims about message content, duration, or transactional completeness.
16.5. Trust Boundaries in Email Headers
An email From field, like a source address in a packet, is not a complete identity proof. RFC 5322 message fields and SMTP transport trace fields play different roles. Received fields are useful for reconstructing a relay path, but the examiner must identify which MTA added each field and where user-controlled data can enter the chain.
Email authentication mechanisms also answer different questions:
- SPF evaluates authorization of sending hosts for specified SMTP identities,
- DKIM cryptographically associates a signing domain with selected message content,
- DMARC uses alignment between the Author Domain and authenticated SPF/DKIM identities together with published policy.
As of 2026, the current base IETF DMARC specification is RFC 9989, with aggregate and failure reporting separated into RFC 9990 and RFC 9991. RFC 7489 remains historically important but is no longer the current base specification.
None of these mechanisms alone proves which human authored a message. Forwarding, mailing lists, re-signing, compromised accounts, and provider architecture still matter.
16.6. Evidence Collection During a DDoS Incident
Incident mitigation and evidence acquisition must not sabotage each other. Full packet capture may be unsustainable at high packet rates; storage or the capture sensor can become an additional bottleneck.
A scalable evidence strategy can combine layers:
flow telemetry            → volume and peer relationships
firewall/load-balancer log→ policy/state behavior
sampled packets           → packet characteristics
bounded full capture      → detail for selected windows
application metrics       → actual service impact
Attack intensity should not be summarized by bit/s alone. Packet/s, new connections/s, concurrent state, application requests/s, CPU, queue depth, and error rate show which resource is actually being exhausted.
In reflection/amplification incidents where spoofing is possible, a source-IP list must not automatically be reported as an attacker list. An observed address may represent a reflector, proxy, compromised node, or spoofed identity. Observation and attribution hypothesis must remain separate.
16.7. Monotonic Time and Wall-Clock Time in Timelines
Wall-clock timestamps are essential in distributed investigations but are not perfect. NTP correction, manual clock changes, VM pause/resume, and time-zone handling can disturb chronology. A process may use a monotonic clock to measure durations, but monotonic values from different machines do not share a common epoch.
Reliable correlation considers:
raw timestamp
+ timezone / offset
+ clock source
+ known skew
+ collection delay
+ ordering constraints
When exact time cannot be established, a report should not invent false precision. Relative ordering or a bounded time interval can be more defensible than an unjustified exact timestamp.
16.8. Provenance and Recomputability of Derived Analytic Findings
A graph, summary, timeline or statistical feature derived from digital evidence does not replace its source material. Every derived finding requires traceability to the source set, time range, filters, algorithm version and parameters. When the association between primary records and computed results is lost, independent verification becomes difficult. Incomplete source material and authorization-limited coverage must be documented explicitly.
For example, a synthetic packet capture with packet loss cannot justify treating a reconstructed TCP stream as a complete session. Likewise, high degree in a temporal graph does not establish a particular intention or criminal relationship between people. Observation, derived metric and interpretation should appear as distinct layers in a forensic report.
Forensic reproducibility requires a precise input definition, transformation sequence and numerical tolerance. If floating-point order or parallel computation may produce slightly different outputs from the same source, the equality criterion should use a justified tolerance rather than assuming byte-for-byte identity.
16.9. Meaning of Failure Classes in Forensic Reporting
Failure to produce an analytic result has at least three different explanations: source data are missing, source data exist but are not accessible, or an auxiliary computation failed. These outcomes cannot all be collapsed into 'no finding'. If timeouts or row limits yield partial coverage, calculated figures must not be labeled as measurements of the full population.
A technical report should separately state the method's validity limits, known sources of error and evidence coverage. This keeps primary evidence, computation success and expert interpretation conceptually distinct.
16.10. Transformation Chains for Derived Evidence
A spectrogram, transcript, or object label derived from an audio or image recording is not the original evidence. Each derived output needs the input identity, tool and version, model parameters, time span, and transformation result. Probabilistic model outputs require a declared decision threshold and a defined human-review boundary.
Conflating file timestamps, event times, and ingestion times can produce a plausible yet causally false timeline. Clock source, timezone, resolution, and synchronization uncertainty should accompany event correlation. Missing metadata must limit the conclusion reported.
Unit 17: Digital Forensic Expert-Witness Duties and Workflow
A digital forensic expert witness examines the assigned specialist or technical questions and submits a reasoned opinion to the appointing authority. Examination uses engineering methods, subject to the limits of the assignment, authorization, and procedural obligations. Applying the law, deciding whether evidence was legally obtained, defining an offense, and determining legal liability belong to the judicial authority.
This unit covers accepting an appointment, conducting examination within authorized boundaries, and professional responsibilities. Unit 18 is the course's sole integrated treatment of report writing.
17.1. Expert-Witness Work and Its Legal Framework
An expert witness is a person or organization asked to provide an opinion on matters requiring expertise or specialist or technical knowledge. Digital forensic expertise may involve storage, operating systems, networks, mobile devices, cloud services, applications, databases, audio, or video. General computer-engineering knowledge does not establish competence in every such specialty.
In Türkiye, the principal rules appear in Expert Witness Law No. 6754, the Expert Witness Regulation, Criminal Procedure Code No. 5271 for criminal proceedings, and Code of Civil Procedure No. 6100 for civil proceedings. Relevant procedural rules also apply in administrative litigation. The legislation in force on the appointment date and the actual appointment order govern the work.
A court-appointed expert report and an opinion commissioned by a party enter a case under different procedures. A party's expert opinion may be considered under CMK 67(6) and HMK 293. A judicial inspection is a separate procedural act performed by the competent authority; participating in it does not confer general investigative powers on the expert. A contractually appointed binding expert (hakem bilirkişi) is another distinct institution. For the technical examiner, the practical questions are who appointed the expert, what may be examined, and to whom must the report be delivered.
The conditions for seeking expert evidence differ between procedural settings. Whether an expert examination is needed and how its findings are weighed are decisions for the competent authority. The expert helps explain factual issues that require specialized knowledge.
17.2. Appointment and Acceptance of the Assignment
Admission to the official register depends on training, professional experience, and the principal and subsidiary fields of expertise. The registered specialties must reflect actual competence. Current conditions are published in the Ministry of Justice's 2026 admission rules. Any obligation to accept appointments arising from registration must be read together with valid grounds for declining or withdrawing under applicable law.
On receiving an appointment, the expert checks:
- Authority and file: Which authority issued the order and for which file?
- Competence: Do the questions fall within the expert's specialties?
- Scope: Are the systems, materials, and periods identified?
- Questions: Are specific, technically answerable questions stated?
- Materials: Are the specified items available physically or through an authorized system?
- Time: Is the deadline compatible with workload, acquisition type, and expertise required?
- Impartiality: Are there grounds for mandatory disqualification, recusal, or challenge?
Perform this check before using examination tools. Notify the appointing authority in writing about omissions or ambiguity. Oaths and acceptance procedures depend on the relevant type of proceeding and expert-witness law; one procedure must not be assumed to fit every appointment.
The technical questions in the order define the expert's scope. An instruction such as “examine all data” should be clarified rather than expanded independently. Specify the requested finding, data source, time window, and expected technical output. If the assignment exceeds the expert's competence, report the limitation and, when necessary, request appointment of another specialist instead of informally redefining the task.
17.3. Expertise and Scope of Authority
A digital forensic expert may make technical findings about file integrity, record structure, temporal relationships, account sessions, network connections, or alterations to content. The expert does not decide whether an act constitutes an offense, whether a person is legally at fault, whether evidence was lawfully obtained, or whether compensation is owed. Expert Witness Law No. 6754 establishes the prohibition on making legal characterizations and evaluations.
Distinguish technical observations from legal judgments:
- Technical finding: An entry of the specified event type exists in the examined records.
- Technical assessment: The entry's source and integrity have been checked, but attribution to a person remains limited.
- Legal judgment: The act constitutes an offense or gives rise to legal liability.
The first two may fall within the authorized expertise when sufficient data exist. The third belongs to the competent judicial authority.
Appointment does not independently authorize access to new accounts, collection of information from third parties, or examination beyond the specified materials. Technical feasibility is not legal authority. Clarify scope before connecting to live systems, obtaining data from remote services, attempting decryption, or performing operations that may change original material.
Information-security, personal-data, and evidence-preservation duties remain relevant after the examination. Not every item found in a case file must be reproduced in the report. Exclude irrelevant personal data while preserving enough necessary information for independent review.
17.4. File Examination and UYAP
First review the appointment order, file attachments, list of materials, and prior technical opinions. The Expert Witness Regulation and official guiding principles provide a framework for using UYAP where available and requesting missing information from the appointing authority.
A first-pass file review produces a concise work plan: questions, materials, required methods, missing records, and risks to the deadline. The plan links work to questions. Give distinct identifiers to versions and copies. A document visible in UYAP, a downloaded local copy, and a physically delivered medium are not automatically the same evidential object.
Prior reports may guide examination but must not be copied without verifying their findings. Identify their underlying data, assess their methods, and compare them with the questions in the new assignment. Where resolution of inconsistent reports is requested, compare observations, methods, and inferences separately.
17.5. Requests for Information and Documents
If essential material is missing, request it precisely. State the record type, relevant period, required fields, which question is affected by the omission, and the requested format. A targeted request is preferable to a general demand for “all logs”; it also supports data minimization and time management.
Request additional documents, a specialist, or a different place of examination through the appointing authority. Do not independently negotiate evidence with the parties or accept material outside the authorized file. Any need to consult the parties must follow the notification and approval process in the official guidance. A private technical discussion with one party, concealed from the other, can compromise impartiality.
Where partial examination is possible, identify the questions that can be answered. Where missing material prevents a reliable conclusion, disclose that fact. The expert must provide a reasoned account of limitations rather than invent certainty for every question.
17.6. Duties During Examination
An expert witness performs the appointed task personally. Independent delegation is not permitted. If another discipline is required, request an appropriate additional appointment. In a panel, members examine issues within their competence and evaluate combined findings together. Reasoned differences of opinion are preserved.
Record material identifiers, seals and packaging, transfer times, identities of custodians, access events, integrity values, and necessary working copies. Units 2–4 cover the underlying technical procedures. The added expert-witness obligation is to maintain an explicit relationship between each examination step and the appointed technical questions.
Keep names and versions of tools, configurations, error records, time zones, and significant transformations in the work record. Do not represent an unverified tool result as independently verified. When live-system operations are necessary, document unavoidable changes and their consequences.
Unexpected findings may arise. Do not expand examination into unrelated data on the expert's own initiative. Informing the appointing authority about a new technical requirement or evidence-preservation concern is different from carrying out an unauthorized investigation.
17.7. Independence, Impartiality, and Confidentiality
An expert's conclusions must not be adjusted to satisfy the appointing authority, parties, or third parties. Define methods in advance and apply the same criteria to the same data and conditions. Disclose limitations of expertise or method. Assess records that contradict a proposed finding as well as those that support it.
Follow the relevant procedure where disqualification, recusal, or challenge grounds exist. Disclose prior professional relationships, financial interests, or other circumstances that could raise reasonable doubts about impartiality. Do not share case files with third parties, personal cloud accounts, or unauthorized analysis services.
Confidentiality requires more than encryption. Plan authorization, access records, retention, secure transfer, minimization of personal data in the report, and handling of working copies after delivery. Under Law No. 6754, confidentiality continues after the appointment ends. The Turkish Personal Data Protection Authority's data-security guidance supports assessment of technical safeguards.
17.8. Deadlines, Fees, and Expenses
Deadlines and extensions depend on the appointment order and applicable procedural rules. If the allocated time becomes inadequate, explain the data volume, acquisition needs, specialist support, and effect of missing evidence. Apply for a reasoned extension before the deadline. Do not apply a time limit from one procedural regime to all others.
For compensation and expenses, consult the 2026 Expert Witness Minimum Fee Schedule and appointment terms. Workload should be explainable through the number of items, data volume, imaging requirements, specialized tools, multidisciplinary work, and examination time. Seek clarification before incurring expenses not authorized in advance.
Effective time management does not mean concealing late delivery or omitting validation to finish early. The appointing authority should learn promptly how time and resource constraints affect the work.
17.9. Expert-Witness Liability
Depending on the conduct and applicable rules, responsibility may be civil, criminal, or disciplinary. Turkish Penal Code No. 5237 includes a specific provision on knowingly false expert evidence. Status in judicial proceedings, confidentiality, failure to perform duties, and professional diligence are governed by the relevant legislation. An erroneous technical interpretation and a knowingly false report are not equivalent legal circumstances.
Engineering risks include exceeding scope, unnecessarily changing original evidence, relying on unvalidated tools, concealing conflicting findings, inventing confidence, omitting missing-data limitations, presenting another person's work as one's own, or disclosing confidential material without authorization.
An auditable work record does not remove liability; it makes the steps and technical grounds transparent. If an error is identified, address the scope and method of correction openly with the appointing authority. The expert's function is not to decide the case but to answer technical questions accurately.
Unit 18: Preparing and Evaluating Expert-Witness Reports
An expert-witness report is the written, reviewable result of a specialist examination. Its purpose is not to reproduce the entire examination log. It connects the appointed questions, evidence, methods, verified findings, and technical opinion in a concise chain of reasoning. A conclusion is only as defensible as the records presented in its support.
This is the course's only dedicated reporting unit. Earlier units explain forensic acquisition, temporal analysis, tool validation, and provenance. Those techniques are not retaught here; the focus is how to document them in an expert-witness report.
18.1. Report Structure and Mandatory Elements
The report's scope depends on the appointing authority, type of case, and applicable procedure. The Expert Witness Regulation, HMK Article 279, and the relevant CMK provisions establish the principal information requirements. The Ministry of Justice's report templates give different examples for different authorities. Differences in form do not remove the need for evidence and method traceability.
At a minimum, organize the appointing authority and file, expert identification, assignment and questions, materials examined, methods, technical findings, reasoned assessment, conclusions, date, signatures, and attachments. In a panel report, describe the allocation of work and any dissenting opinion.
A good forensic report is not a collection of screenshots. A reader should be able to determine:
- what material was examined,
- which tools and methods were used,
- how source integrity was protected,
- which observations were made,
- which inferences were drawn,
- which alternative explanations remain,
- what the limitations are,
- how another examiner can reproduce the result.
Each section answers a distinct question: the assignment explains why, materials explain what, methods explain how, findings explain what was observed, and conclusions explain which technical question was answered and to what extent.
18.2. Appointment Details and Examination Questions
The opening section identifies the date of the order, case number, examination boundaries, and questions. Instead of copying lengthy passages from the order, state the actual technical questions that govern the work. Cite written authorization for any permitted change of scope.
Questions may use stable identifiers such as Q-01 and Q-02. This convention is a traceability aid, not a formal legal requirement. Each question should link to its materials, methods, findings, and answer. Do not insert an unsolicited legal conclusion.
If the assignment spans several specialties, distinguish the examination performed personally from tasks allocated to other experts. Do not conceal an ambiguous or unanswerable question; state the technical reason beneath the relevant question.
18.3. Examined Materials and Methods
Identify materials without ambiguity. For each item, record its type, source, distinguishing identifier, delivery state, relevant size or scope, receipt date, and available integrity-verification details. A removable card, device-internal storage, and a cloud account are not a single evidence item. Maintain consistent identifiers throughout the report.
Identifiers such as M-01, M-02, and D-01 may be used. Original media, forensic images, exports, reconstructed files, and analytical outputs are separate evidence types. When a digest is reported, identify its algorithm, byte range, and exact object. Matching SHA-256 digests support a defined integrity check; they do not prove original creation conditions, truth of content, or identity of a physical user.
Describe methods sufficiently for independent review: tool name and version, relevant settings, commands or operation types, time zone, parsing approach, filters, selection criteria, and verification step. “Examined using forensic software” is inadequate. Do not imply independent validation when none was performed.
If there are read errors, partial images, locked volumes, corrupted records, missing logs, or losses during conversion, identify the affected region and effect on results. These details establish the limits of a conclusion.
18.4. Examination Steps and Technical Findings
Present observations before expert inferences. Relate every finding to the relevant question and evidence identifier. A screenshot or automatically generated report does not substitute for an explanation of the method. Identify the raw source location, parsing procedure, and second verification method where needed.
A technical finding should separate four elements:
- Source: which evidence item and location?
- Observation: what was present in the raw or parsed data?
- Method: what tool or procedure produced the observation?
- Interpretation: what does the observation mean for the case?
For example:
Source        : Disk image D1, user-profile artifact
Observation   : A record exists at 14:32:11Z
Method        : Parsed with Tool A; raw record verified independently
Interpretation: Supports possible interaction by the relevant account
Limit         : Does not independently identify the physical user
When several sources appear to corroborate a finding, their independence must be assessed. A transcript and a topic summary generated from that transcript are not two independent observations. Separating original evidence, derived analysis, and examiner judgment allows later reviewers to revisit an interpretation without confusing it with the source material.
A transcript, keyword list, and automated summary derived from the same audio recording are not three independent sources. They share provenance. Metadata within a file and a separate server's transfer log may provide distinct observations, but actual independence should be verified.
Findings should be checkable by another qualified examiner at the required level. If an observation depends on a single tool, explain its limitations. Where parsers disagree, give the grounds for selecting a particular result or version.
18.5. Assessment of Findings
Observation:
  A record exists with timestamp 2026-09-23T10:15:04+03:00.

Interpretation:
  The record supports the possibility that the application was active then.

Overclaim:
  The user definitely opened the application at that exact moment.
The discipline of digital forensics lies partly in resisting the third sentence.
Likewise, two communications occurring close in time do not establish a causal link. Mentions of the same name in different transcripts do not necessarily identify one person. Alternative explanations—name collisions, incorrect timezone conversion, or incomplete collection scope—should be tested separately from the observed records.
Assessment links observed data to a technical account of the event. A logged-in account and the physical person operating it are different inferences. A shared IP address cannot alone identify a person in NAT or CGNAT environments. A timestamp discrepancy may result from synchronization or copying rather than deliberate alteration.
Identify supporting records, assumptions, and alternative explanations for every interpretation. Leave unresolved alternatives explicit when data are missing. A non-calibrated score must not become a claim such as “95% certain.” In audio, video, and AI-assisted examination, disclose methodological validity and false-positive risks.
18.6. Conclusions and Expert Opinion
The conclusion introduces no new evidence. It converts previously verified findings into answers to the appointed questions, in their original order. Each answer states the observed condition, its technical basis, and its limitations. Questions that cannot be answered receive the same explicit treatment.
Excessively strong language weakens an expert report. “The specified entries were found” establishes the presence of records. “A named person performed the operation” requires independently supported attribution. A technical expert must not infer criminal culpability, fault, legal admissibility, or legal responsibility from a technical artifact alone.
A simple test of a reasoned opinion is whether a second expert, given the same question, can challenge every technical assertion through the evidence, method, and observation cited. If not, repair the technical links before delivery.
18.7. Attachments and References
Attachments contain records necessary to support the report: relevant parsed output, screenshots, validation records, inventories, integrity checks, or limited exports. More attachments do not inherently make the report stronger. Identify each attachment's name, format, origin, relevant digest, and linked finding identifier where applicable.
Attachment organization must preserve evidence identity. Avoid ambiguous names such as “the phone concerned” when several devices are examined. Material M-02 remains M-02 in every annex. For large files, state whether the files are delivered physically or electronically and distinguish that delivery from the original examination material.
Cite scientific and technical references for the methodological statements they actually support. A standard or guide that provides technical principles is not automatically a binding legal rule in every proceeding in Türkiye. The Ministry of Justice reporting guidance emphasizes clarity and reasoned explanations.
18.8. Clear Language and Auditability
Use short sentences, explicit evidence identifiers, and measurable observations. Prefer “The item was examined” to unnecessarily elaborate passive expressions. Define essential technical terms on first use. Use abbreviations consistently. The report must not read as advocacy for either party.
A good technical statement identifies the source and scope of an observation:
- “The compared records within the defined data interval of
M-01match.” - “Integrity of the exported records within the source system at the time of initial creation could not be established from the available material.”
- “No entry of the requested type was identified during the stated interval; the conclusion is limited to the supplied records because retention coverage could not be verified.”
- “Two parsers produced different outputs; the conflicting fields were excluded from the definitive opinion.”
Methods should remain reproducible. That does not mean placing every processing log in the body; extensive logs belong in attachments. The main text presents only the relevant observations, verification, and limitations. Readability and technical auditability must coexist.
18.9. Signatures, Delivery, and Return of Materials
Before submission, check all assigned questions, references between text and annexes, technical grounds, page and attachment counts, evidence identities, confidentiality, and any dissent. Submit through the channel specified by the authority. Where UYAP submission is required, use the relevant expert system, electronic signature, and delivery procedures.
Specify the type, quantity, and integrity information for attachments supplied physically or electronically. Return physically received material with an inventory and a documented transfer. Confidentiality continues after delivery. Retention or disposal of unnecessary working copies follows applicable authorization and retention rules; the expert must not independently disclose them.
18.10. Objections, Supplementary Reports, and Explanations
The appointing authority evaluates the report; an expert opinion is not a judicial judgment. Objections, requests for clarification, and supplementary reports follow different procedural rules. HMK Articles 281–282 govern evaluation and objections in civil proceedings; their time limits do not automatically apply in criminal cases. Criminal proceedings follow the relevant CMK provisions and the competent authority's orders.
On receiving a request for a supplementary report, first determine how the new question relates to the original assignment and its scope. Distinguish new evidence, corrected methods, disclosed errors, and any changed opinion. Address the requested technical deficiency instead of repeating the entire initial report; explain any resulting change to the conclusion.
Conflicting expert reports are compared by their data, methods, and assumptions, not the titles of their authors. Review the supporting technical material before endorsing or rejecting another report. When called to explain findings at a hearing, the expert stays within direct observations and professional competence.
18.11. Reporting Template and Quality Control
The following is an engineering work outline, not a substitute for an official report template. It contains no real identities, events, or case details.
EXPERT-WITNESS REPORT

Appointing authority : [Competent authority]
Case identifier      : [Case details]
Appointment date     : [Date]
Expert identification: [Identity, specialty, registration]
Report date          : [Date]

1. TASK AND QUESTIONS
   Q-01: [First technical question]
   Q-02: [Second technical question]

2. EXAMINED MATERIALS
   M-01: [Type, source, identifier, receipt information]
   M-02: [Type, source, identifier, receipt information]
   [Originals, copies, integrity, and missing-material notes]

3. METHOD
   [Tools, versions, operations, time zone, validation]
   [Method limitations and errors]

4. TECHNICAL FINDINGS
   F-01: [Verifiable observation linked to M-01]
   F-02: [Verifiable observation linked to M-02]

5. ASSESSMENT
   [Technical meaning of the observations]
   [Alternative explanations and uncertainties]

6. CONCLUSIONS AND OPINION
   Q-01: [Answer supported by findings and limitations]
   Q-02: [Answer supported by findings and limitations]

7. ATTACHMENTS
   A-01: [Attachment linked to F-01 and delivery method]
   A-02: [Attachment linked to F-02 and delivery method]

[Signature and mandatory formal elements]
Pre-delivery checklist:
- Has every appointed question been answered or its unresolved status explained?
- Does every material have one unique and consistent identifier?
- Are original evidence, forensic images, and derived analysis distinguished?
- Are digest algorithms, objects, and verification scopes stated?
- Can tools, versions, relevant parameters, and methods be explained?
- Are observations, interpretations, and legal conclusions kept separate?
- Can each technical conclusion be traced back to data and validation?
- Are missing data, divergent outputs, and method limitations disclosed?
- Are identities, names, and times consistent between the report and annexes?
- Were confidentiality, signatures, delivery, material returns, and deadlines checked?
The quality of a report is measured not by its length but by whether the answers are reasoned and verifiable. Avoiding duplicate technical explanations across units is also a structural principle of this course.
References
- Albert-László Barabási. Network Science.
- Burucu, E.; Özer, Ö. "Adli Konuşmacı Tanıma İncelemelerinde Ses Sahteciliği." Uluslararası Bilgi Güvenliği Mühendisliği Dergisi, 1(1), 20–26, 2015. https://doi.org/10.18640/ubgmd.192662
- Carrier, B. File System Forensic Analysis. Addison-Wesley, 2005.
- Casey, E. Digital Evidence and Computer Crime: Forensic Science, Computers, and the Internet. 3rd ed., Academic Press, 2011.
- Celozzi, Salvatore; Araneo, Rodolfo; Lovat, Giampiero. Electromagnetic Shielding. Wiley-IEEE Press, 2008. ISBN 978-0-470-05536-6.
- Davis, S. B.; Mermelstein, P. "Comparison of Parametric Representations for Monosyllabic Word Recognition in Continuously Spoken Sentences." IEEE Transactions on Acoustics, Speech, and Signal Processing, 1980. https://doi.org/10.1109/TASSP.1980.1163420
- de Cheveigné, A.; Kawahara, H. "YIN, a Fundamental Frequency Estimator for Speech and Music." Journal of the Acoustical Society of America, 2002. https://doi.org/10.1121/1.1458024
- Hermansky, H. "Perceptual Linear Predictive (PLP) Analysis of Speech." Journal of the Acoustical Society of America, 1990. https://doi.org/10.1121/1.399423
- Hjelmvik, E. NetworkMiner 3.2 Source Code: PacketParser and PacketHandlerFramework. NETRESEC.
- IETF. RFC 5322, Internet Message Format. https://www.rfc-editor.org/info/rfc5322
- IETF. RFC 6376, DomainKeys Identified Mail (DKIM) Signatures. https://www.rfc-editor.org/info/rfc6376
- IETF. RFC 7208, Sender Policy Framework (SPF) for Authorizing Use of Domains in Email, Version 1. https://www.rfc-editor.org/info/rfc7208
- IETF. RFC 9293. Transmission Control Protocol (TCP). https://www.rfc-editor.org/rfc/rfc9293
- IETF. RFC 9989, Domain-Based Message Authentication, Reporting, and Conformance (DMARC). https://www.rfc-editor.org/info/rfc9989
- IETF. RFC 9990, DMARC Aggregate Reporting. https://www.rfc-editor.org/info/rfc9990
- IETF. RFC 9991, DMARC Failure Reporting. https://www.rfc-editor.org/info/rfc9991
- ISO/IEC 27037:2012. Guidelines for identification, collection, acquisition and preservation of digital evidence. https://www.iso.org/standard/44381.html
- ISO/IEC 27041:2015. Guidance on assuring suitability and adequacy of incident investigative method. https://www.iso.org/standard/44405.html
- ISO/IEC 27042:2015. Guidelines for the analysis and interpretation of digital evidence. https://www.iso.org/standard/44406.html
- ISO/IEC 27043:2015. Incident investigation principles and processes. https://www.iso.org/standard/44407.html
- Kim, C.; Stern, R. M. "Power-Normalized Cepstral Coefficients (PNCC) for Robust Speech Recognition." IEEE/ACM Transactions on Audio, Speech, and Language Processing, 2016. https://research.google/pubs/power-normalized-cepstral-coefficients-pncc-for-robust-speech-recognition/
- Marmara University. Forensic Examination and Analysis of Computer-Based Cybercrime. Graduate thesis listing, 2013. https://avesis.marmara.edu.tr/yonetilen-tez/e92e7b8a-0983-452a-8b5c-9e4242d1395f/bilgisayar-tabanli-bilisim-suclarinin-adli-bilisim-cercevesinde-incelenmesi-ve-analizi
- Ministry of Justice, Directorate of Expert Witnesses. 2026 Minimum Fee Schedule for Expert Witnesses. December 26, 2025. https://bilirkisilik.adalet.gov.tr/Home/SayfaDetay/2026-yili-bilirkisilik-asgari-ucret-tarifesi26122025021116
- Ministry of Justice, Directorate of Expert Witnesses. Admission Requirements and Procedures for the Expert Witness Register. January 22, 2026. https://bilirkisilik.adalet.gov.tr/Home/SayfaDetay/bilirkisilik-siciline-kabule-iliskin-usul-ve-esaslar22012026125519
- Ministry of Justice, Directorate of Expert Witnesses. Basic Expert Witness Training Coursebook. May 2025. https://bilirkisilik.adalet.gov.tr/Home/SayfaDetay/bilirkisilik-temel-egitimi-kaynak-kitabina-iliskin-duyuru15052025083838
- Ministry of Justice, Directorate of Expert Witnesses. Checklist for Expert Witnesses. https://bilirkisilik.adalet.gov.tr/Home/SayfaDetay/bilirkisiler-icin-kontrol-listesi14032022105444
- Ministry of Justice, Directorate of Expert Witnesses. Expert Witness Regulation. Including May 3, 2025 amendments. https://bilirkisilik.adalet.gov.tr/Resimler/SayfaDokuman/80820251051147.5.23818.pdf
- Ministry of Justice, Directorate of Expert Witnesses. Expert Witness Report Templates. https://bilirkisilik.adalet.gov.tr/Home/SayfaDetay/bilirkisi-rapor-sablonlari14032022105509
- Ministry of Justice, Directorate of Expert Witnesses. Guiding Principles for Expert Witnesses and Required Standards for Expert Reports. April 6, 2026. https://bilirkisilik.adalet.gov.tr/Resimler/SayfaDokuman/20260406170009026Bilirki%C5%9Filerin%20Uyaca%C4%9F%C4%B1%20Rehber%20%C4%B0lkeler%20ve%20Bilirki%C5%9Fi%20Raporlar%C4%B1nda%20Bulunmas%C4%B1%20Gereken%20Standartlar.pdf
- Ministry of Justice. Code of Civil Procedure No. 6100. UYAP Legislation. https://mevzuat.adalet.gov.tr/mevzuat/103103
- Ministry of Justice. Criminal Procedure Code No. 5271. UYAP Legislation. https://mevzuat.adalet.gov.tr/mevzuat/102946
- Ministry of Justice. Expert Witness Law No. 6754. UYAP Legislation. https://mevzuat.adalet.gov.tr/mevzuat/104136
- Ministry of Justice. Turkish Penal Code No. 5237. UYAP Legislation. https://mevzuat.adalet.gov.tr/mevzuat/103228
- NIST SP 800-101 Rev. 1. Guidelines on Mobile Device Forensics. https://csrc.nist.gov/pubs/sp/800/101/r1/final
- NIST SP 800-86. Guide to Integrating Forensic Techniques into Incident Response. https://csrc.nist.gov/pubs/sp/800/86/final
- NIST. Computer Forensics Tool Testing Program (CFTT). https://www.nist.gov/itl/ssd/software-quality-group/computer-forensics-tool-testing-program-cftt
- NIST. Computer Forensics Tools & Techniques Catalog. https://toolcatalog.nist.gov/
- NIST. FIPS 180-4: Secure Hash Standard, 2015. https://csrc.nist.gov/pubs/fips/180/4/upd1/final
- Petter Holme; Jari Saramäki (eds.). Temporal Network Theory. 2nd ed. Springer Nature Switzerland, 2023.
- Scientific Working Group on Digital Evidence (SWGDE) "Best Practices for Enhancement of Digital Audio, 20-A-001-2.0." SWGDE, 2025. https://www.swgde.org/documents/published-complete-listing/20-a-001-2/
- Scientific Working Group on Digital Evidence. Best Practices for Digital Evidence Acquisition, Preservation, and Analysis from Cloud Service Providers, Version 1.1, 2025. https://www.swgde.org/documents/published-complete-listing/23-f-004-best-practices-for-digital-evidence-acquisition-preservation-and-analysis-from-cloud-service-providers/
- Scientific Working Group on Digital Evidence. Best Practices for Digital Evidence Collection, Version 2.0, 2025. https://www.swgde.org/documents/published-complete-listing/18-f-002-2-0/
- Todisco, M.; Delgado, H.; Evans, N. "A New Feature for Automatic Speaker Verification Anti-Spoofing: Constant Q Cepstral Coefficients." Odyssey 2016, 2016. https://www.isca-archive.org/odyssey_2016/todisco16_odyssey.pdf
- Turkish Justice Academy (hosting institution). Digital Evidence Guide. Council of Europe, version 3.0, 2022. https://kanuni.taa.gov.tr/assets/dosyalar/Dijital_Delil_Kilavuzu_WEB.pdf
- Turkish Personal Data Protection Authority. Data Security Obligations. https://www.kvkk.gov.tr/Icerik/2040/Veri-Guvenligine-Iliskin-Yukumlulukler
- W3C. PROV-O: The PROV Ontology. W3C Recommendation, 2013. https://www.w3.org/TR/prov-o/
- Zahra Zohrevand; Uwe Glässer. Should I Raise The Red Flag? A Comprehensive Survey of Anomaly Scoring Methods toward Mitigating False Alarms. arXiv, 2019. https://arxiv.org/abs/1904.06646